Why Board Meetings and Executives Are Targets
Senior people combine authority with exposure. A director or chief executive can authorize payments, approve deals and request confidential documents, and their faces and voices are widely available in earnings calls, investor days, interviews and conference videos. That public material is what voice cloning and face-swap tools need.
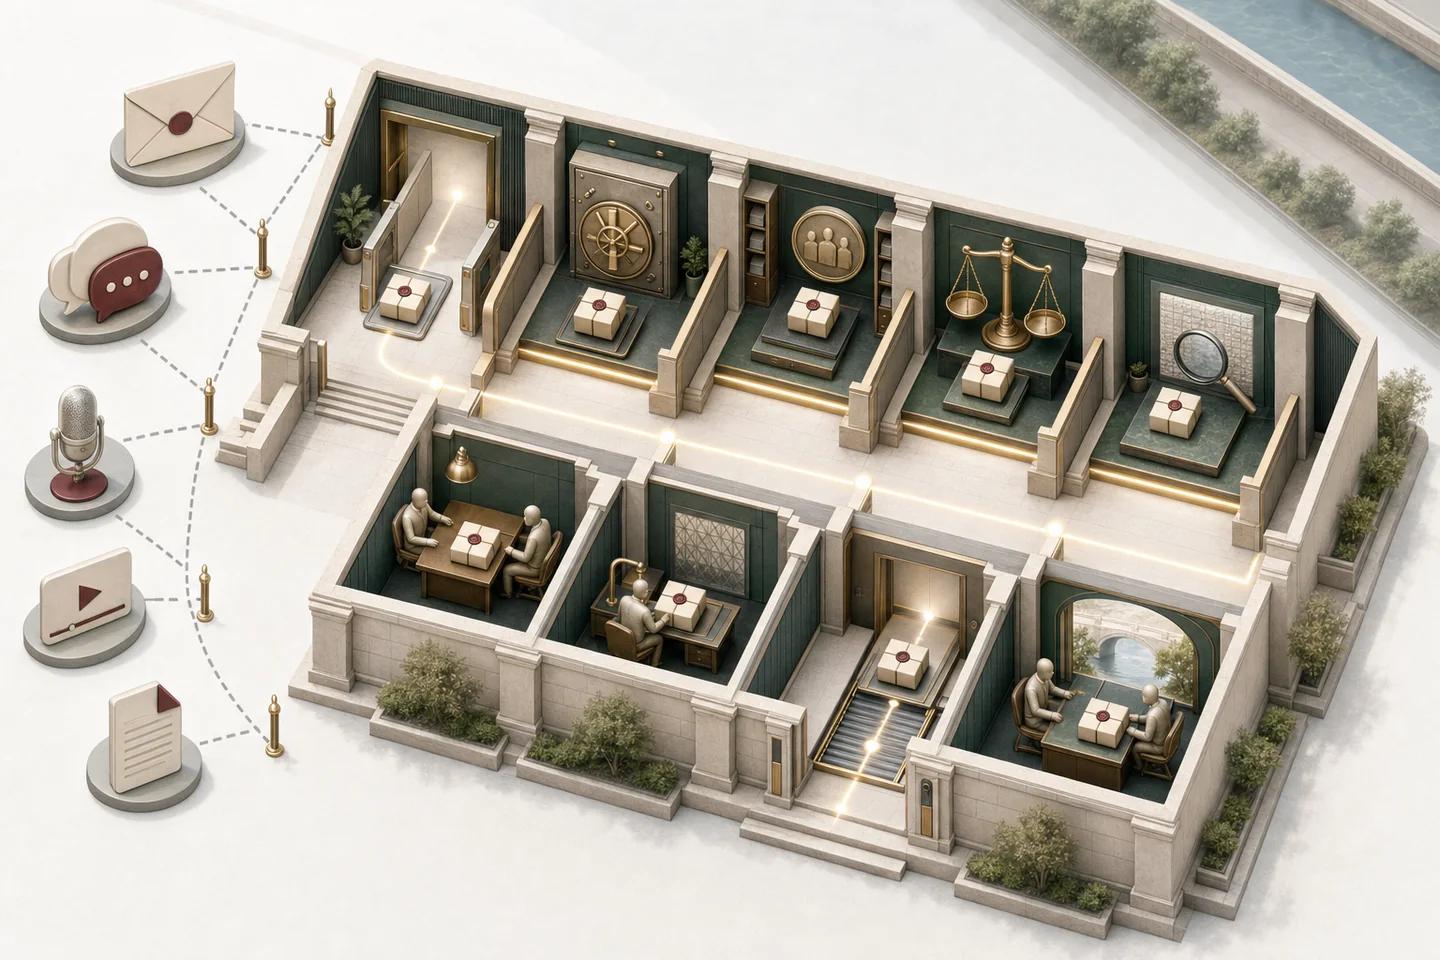
Remote governance adds openings. Board and committee meetings now often run on video, papers arrive by email, and urgent matters are handled by message between meetings. Each channel can be impersonated: a fake invite to an emergency session, a cloned voice note from the chair, or a video call where one participant is not who they appear to be.
Attackers also choose timing. Requests tend to arrive when the real person is travelling, in another time zone or known to be busy, often during a live deal or reporting period when urgency feels normal and confidentiality is expected. Those same conditions make staff less likely to call back and check. Boards can blunt this by agreeing in advance which channels are used for urgent matters and making it clear that a callback to confirm a request is always welcome, however senior the person asking.
What the Arup Case and FBI Warnings Show
The most cited case involved a whole meeting. Hong Kong police said in February 2024 that a finance worker joined a video call with people he believed were the company's chief financial officer and other staff, all of them deepfake re-creations. He had first suspected a phishing email asking for a secret transaction, but set his doubts aside because the people on the call looked and sounded like colleagues he knew. In May 2024 Arup confirmed to CNN that it was the company involved and that fake voices and images were used; according to police cited by RTHK, HK$200 million was sent in 15 transactions.
Government officials face the same technique. The FBI warned on 15 May 2025 that since April 2025 malicious actors had been impersonating senior US officials with text messages and AI-generated voice messages, targeting current and former officials and their contacts to build rapport before sending malicious links. Its advice was blunt: do not assume a message claiming to be from a senior official is authentic.
The lesson for boards is that recognition is no longer verification. A familiar face and voice, even several of them on one call, do not prove who is speaking.
Meeting Controls Before and During the Call
Basic video conferencing security still matters. CISA's guidance on securing video conferencing asks organisations to manage risk at both organisational and user level. For boards that translates into a short list:
- Send invites only from the company secretary's calendar or the board portal, and treat any invite from another source as suspect.
- Use unique meeting links and a lobby, with a host who admits only attendees on the published list and confirms anyone joining from an unknown device or name.
- Agree in advance that directors keep cameras on and join from their usual accounts; a director who suddenly joins audio-only from a new number should be confirmed by callback.
- Never share board papers, deal terms or passwords in the meeting chat; use the board portal.
- Record meetings where policy and law allow, so a disputed instruction can be examined afterwards.
Decision Rules That Make Impersonation Pointless
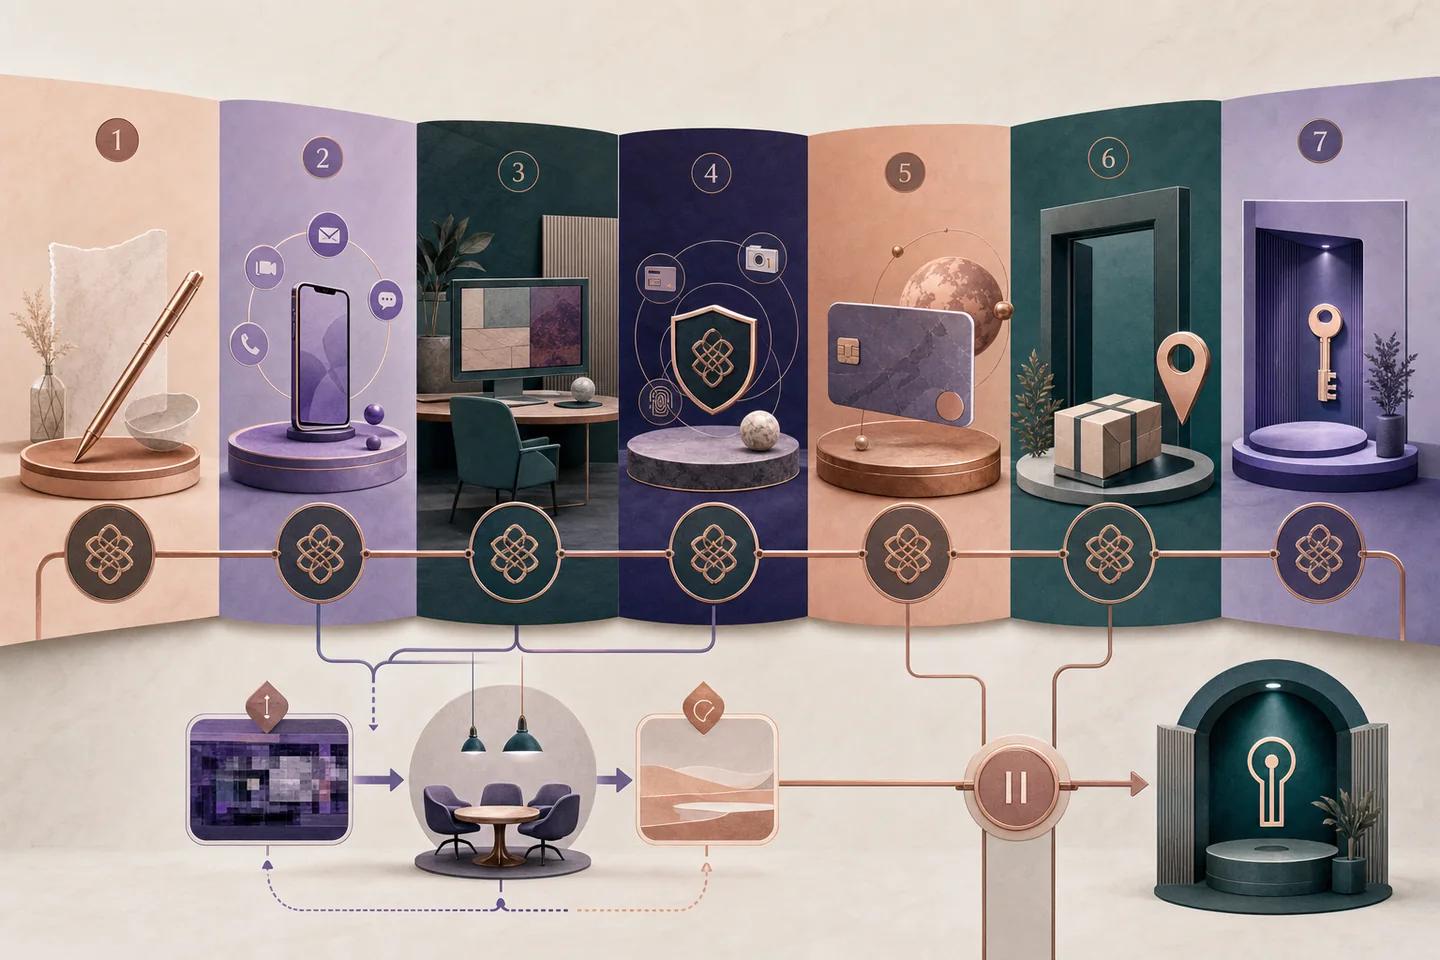
Detection can fail, so the strongest control is procedural. If no instruction given on a call is executed until it is confirmed elsewhere, a perfect deepfake still achieves nothing. Write the rule into the board's operating procedures and the finance team's payment policy, and rehearse it.
| Request | Risk if impersonated | Confirm through |
|---|---|---|
| Payment or fund transfer | Direct financial loss | Payment system approval workflow with two authorized approvers, plus callback to a number on file |
| Board resolution or approval | Unauthorized corporate action | Signed written resolution or vote recorded in the board portal |
| Request for confidential papers | Leak of deal or market-sensitive information | Access only through the board portal with the director's own login |
| Urgent change of meeting or adviser | Attacker controls the next interaction | Company secretary confirms by phone using known numbers |
| Voice note or message from the chair | Rapport building before a malicious link | Reply in a separate, established channel before acting |
Where Deepfake Detection Helps and Where It Stops
Detection is most useful after the fact and at the margins: examining a recording when someone questions what was said, checking a voice note before replying, or reviewing a suspicious video message from an executive. It gives the security team evidence to support a decision to freeze a payment, warn the board or report to police.
It does not replace the decision rules above. Live video is compressed and variable, and a good real-time face swap on a poor connection can be hard to call with confidence in the moment. A clean result also does not prove an instruction is legitimate, because a real executive can be coerced or can make a mistake. Use detection to inform, and process to protect.
Examining Suspect Meeting Media With NeuroDetect
NeuroDetect is Neural Defend's forensic media workspace. A security analyst uploads the authorized recording, voice note, video message or image into a case. The analysis keeps model and version context and shows the original alongside explainability heatmaps and attention views, down to the video frames, face regions and audio segments that carry signs of manipulation. An LLM-assisted summary explains the findings in plain language linked to the evidence, and the analyst makes the final call.
The case exports as a forensic report covering observations, uncertainty, provenance, model context and analyst notes, which is the package a general counsel, an insurer or the police will ask for. Organisations with strict confidentiality rules can deploy NeuroDetect in a private cloud, on premises or air-gapped, and Neural Defend holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certifications. For checking a face image or short clip inside an internal tool, NeuroVerify returns six signals in one API call in under 200 ms at p95 on eligible image requests.
Evidence boundary
Limitations
- Real-time detection on compressed live video is harder than forensic review of a recording, so procedural confirmation remains the primary control.
- A clean detection result does not show that an instruction is legitimate; coerced or mistaken genuine executives pass media checks.
- Recording meetings for later review must comply with company policy and local consent and privacy law.
- Case details for Arup come from the company's statement to CNN and Hong Kong police reports, not a published investigation.
Source record
Sources and references
- CNNArup revealed as victim of $25 million deepfake scam involving Hong Kong employeePublished May 16, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterSenior US Officials Impersonated in Malicious Messaging CampaignPublished May 15, 2025. Verified October 19, 2026.
- Cybersecurity and Infrastructure Security AgencyGuidance for Securing Video ConferencingPublished January 7, 2021. Verified October 19, 2026.
- National Institute of Standards and TechnologyNIST AI 100-4, Reducing Risks Posed by Synthetic ContentPublished November 20, 2024. Verified October 19, 2026.