

Neural Defend

Deployment Security

Neural Defend's public Website Privacy Policy does not identify production regions, disaster-recovery regions, tenancy, network design, or a deployment-specific control set. Those details depend on the proposed service and customer agreement and should be confirmed directly with Neural Defend.

Maintained byNeural Defend Editorial
Updated August 9, 2026
Piyush Verma, Co-founder and CEO of Neural Defend.
Piyush VermaCo-founder & CEO
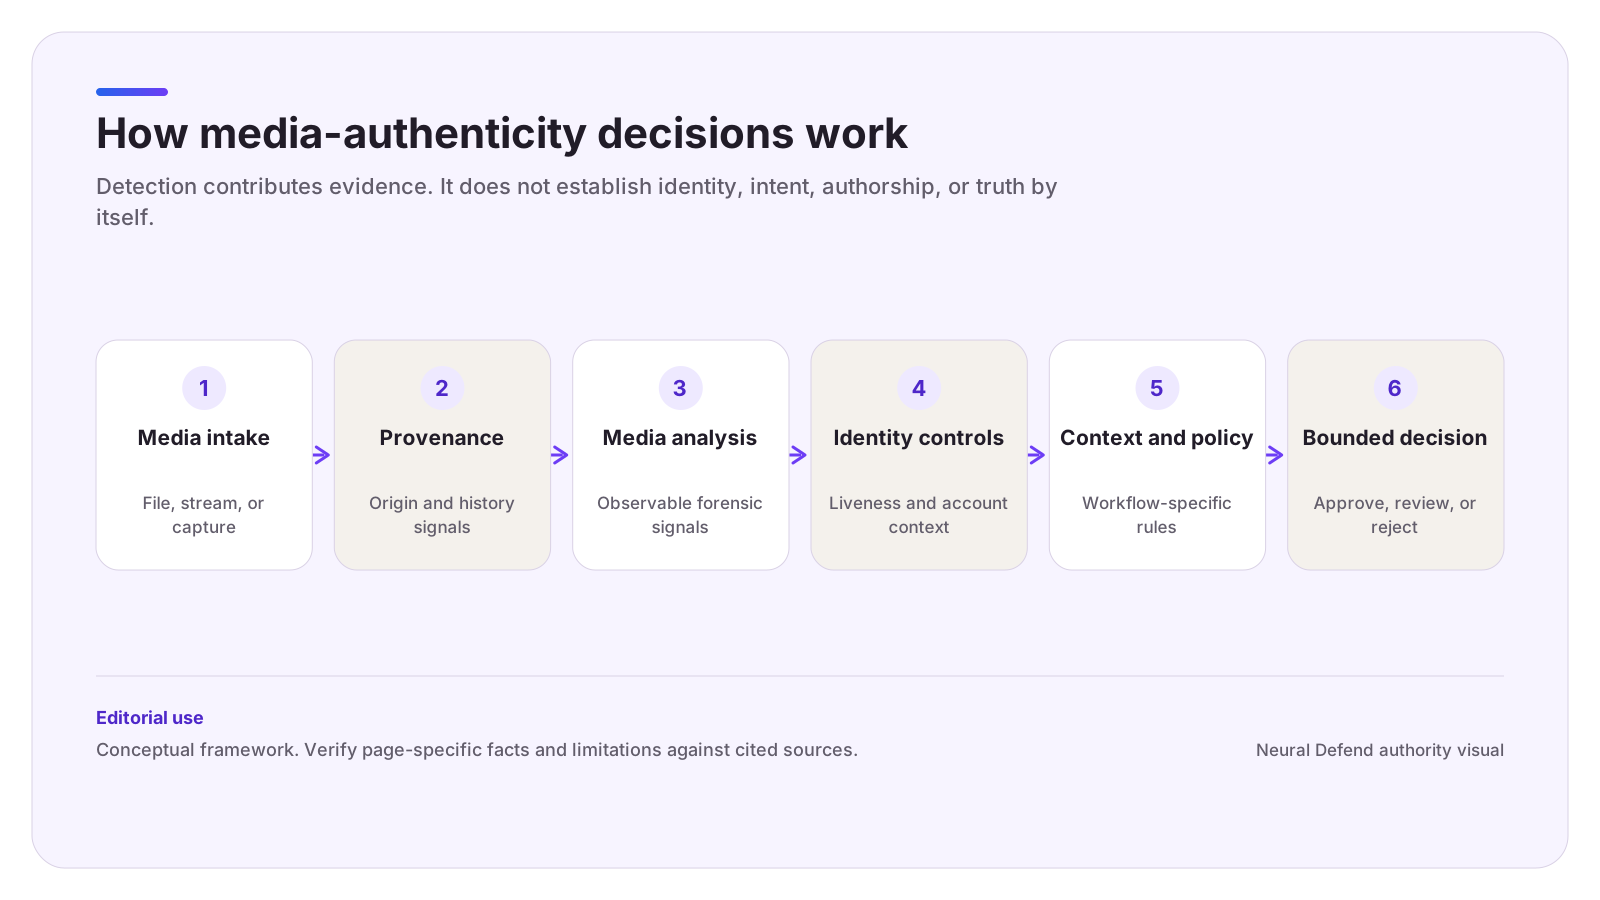
A six-stage flow separates media intake, provenance, signal analysis, identity checks, context and policy, and the final bounded decision.Category visual

Published deployment statements

The Website Privacy Policy intentionally avoids publishing unverified hosting regions or deployment-specific control claims. It provides a general safeguard statement and directs customer-specific processing and retention questions to the applicable agreement and Data Processing Addendum.

What to confirm before deployment

Ask for the architecture and responsibilities that apply to the selected product and environment. Public sources do not specify tenancy, network boundaries, key ownership, recovery objectives, environment access, support access, or evidence packages for each deployment model.

Evidence boundary

Limitations

  • No deployment architecture or customer responsibility matrix is publicly cited on this page.

Source record

Sources and references

  1. Neural DefendWebsite Privacy PolicyVerified August 7, 2026.

Architecture review

Discuss your deployment

Share the proposed product, region, hosting model, and assurance requirements with Neural Defend.

Contact Neural Defend