
Open account → Capture ID → Selfie and liveness → Face match → Screening → Decision
A manipulated selfie that clears liveness and face match reaches screening as if it were a genuine customer. Nothing in the journey scored authenticity.
eKYC / NeuroVerify
Banks, fintechs and identity teams in any country run remote selfie checks at onboarding. Attackers now answer those checks with face swaps, synthetic faces and injected video. NeuroVerify checks the same selfie for deepfakes and manipulation beyond liveness, in one API call.
It fits the selfie and liveness step you already run: send the media you already capture, with no new step for the end user, and get one unified risk score with signal-level evidence.
NeuroVerify does not replace your identity proofing, document checks or policy. It adds authenticity evidence for the face and video your journey already collects.
The gap
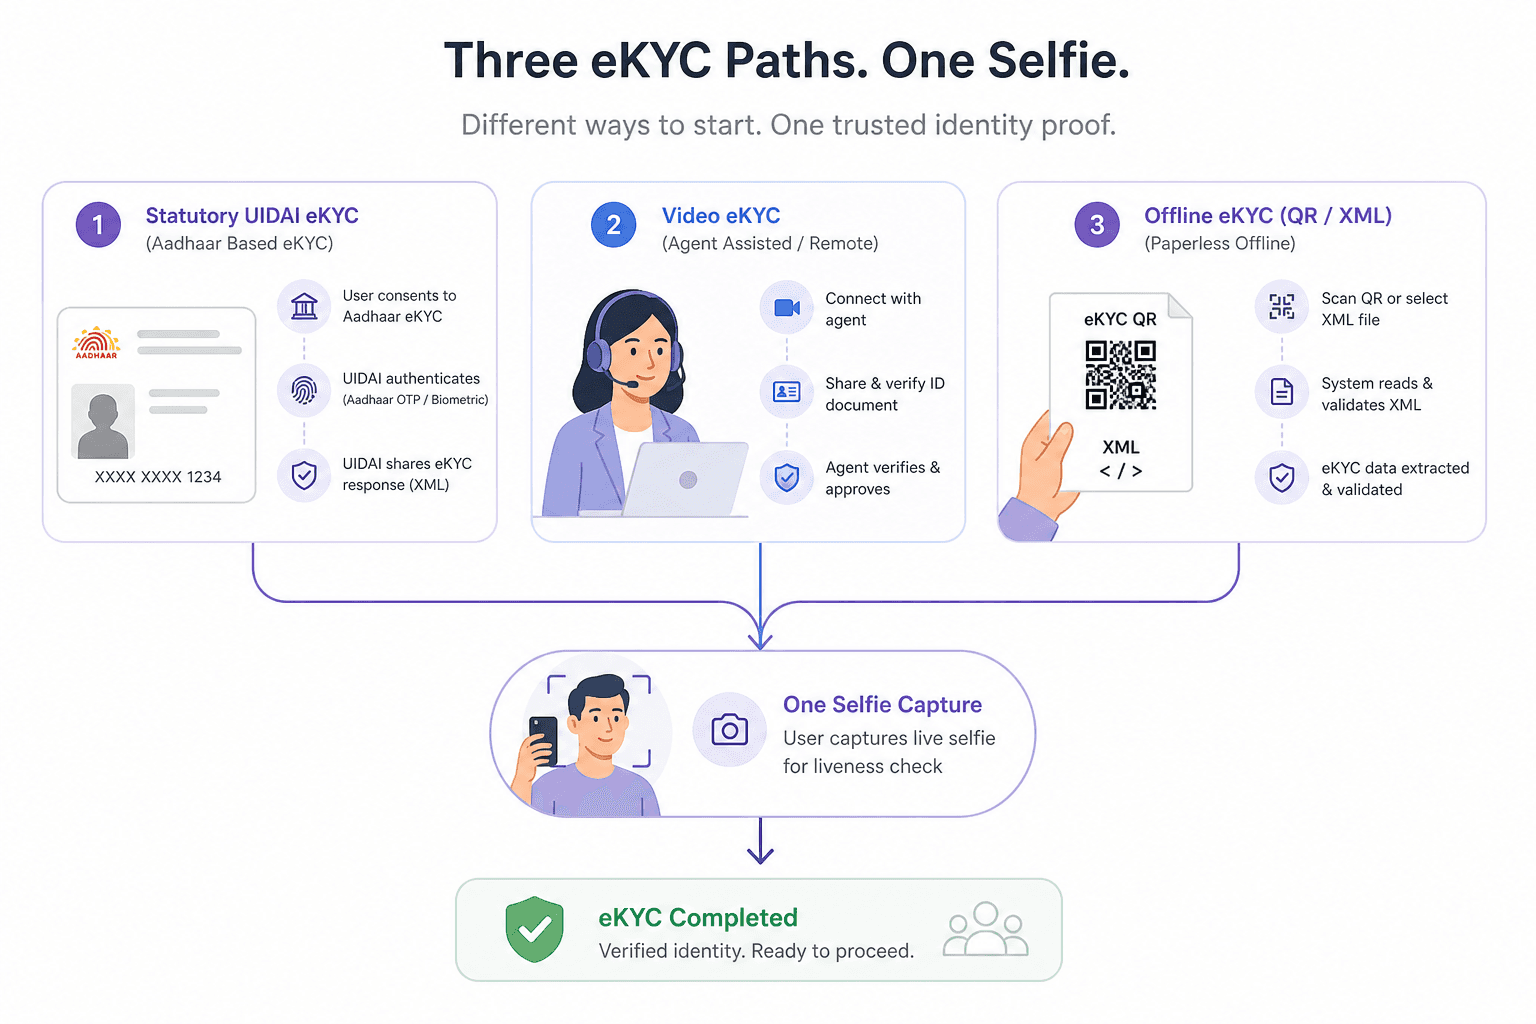
Remote eKYC usually chains a few controls: capture an ID document, take a selfie with a liveness prompt, match the face to the document portrait, then screen the applicant against watchlists and registries. Each control answers a narrow question. None of them asks whether the selfie itself was generated or altered.
Liveness checks whether a live person appears to be in front of the camera. Face match checks whether two faces look alike. A deepfake can satisfy both: a face-swapped video can respond to a prompt, and a synthetic portrait can match a stolen document photo closely enough to clear a threshold.
Open account → Capture ID → Selfie and liveness → Face match → Screening → Decision
A manipulated selfie that clears liveness and face match reaches screening as if it were a genuine customer. Nothing in the journey scored authenticity.
Standards bodies treat this as a live concern. FATF digital identity guidance expects institutions to understand the assurance level of the identity systems they rely on. See FATF Digital Identity Guidance and How Deepfakes Exploit KYC Verification Systems.
Threats
These are attack techniques, not claims about any specific institution. Each one targets the selfie and video evidence rather than the registry record.
The attacker maps a victim's face onto their own in real time during the liveness prompt. Blink, turn and smile challenges can be followed while the face on screen is not theirs.
Software replaces the device camera feed with pre-recorded or generated video. The app sees a normal stream, so on-device checks never see the physical camera. See Digital Injection Attacks.
A generated face is paired with a fabricated or stolen identity to open accounts that never belonged to a real person. See Synthetic Identity Fraud.
An attacker edits or generates a selfie so it resembles the portrait on a stolen document. Face match passes because the two faces are close, not because the person is genuine.
A real customer's earlier selfie or video is replayed into a new attempt. The face is real, but it is not live and not this person's session now. See Replay Attacks in Identity Proofing.
Fraud rings reuse generated faces and automation to open many accounts quickly. Each application looks clean on its own.
These threats are one reason regulators and standards bodies are asking more of remote identity proofing. See FinCEN Deepfake Fraud Alert and eIDAS and EUDI Wallet Identity Proofing.
Detection evidence supports your controls. Your own policy and your regulator's requirements decide what counts as sufficient.
Where NeuroVerify fits
NeuroVerify sits after the selfie is captured and before your policy acts. Your identity provider keeps document checks, face match and screening. NeuroVerify adds one question they do not ask: is this face, video or audio authentic?
Capture ID → Selfie and liveness → Face match → Decision
Liveness passes, face match passes, and a deepfake is approved.
Capture ID → Selfie → NeuroVerify risk score → Face match → Decision with evidence
One call is added. Nothing is removed.
Six signals run in a single request: Visual Safety Screening, Live Presence Verification, Face Manipulation Detection, AI Generative Model Analysis, AI Pixel-Level Manipulation and AI Content Compliance. They resolve into one unified risk score, with signal-level evidence your reviewers and policy engine can use. See NeuroVerify and KYC solutions.
Your eKYC provider, document verification, face match, screening and decisioning stay where they are. NeuroVerify supplies authenticity evidence. Your policy makes the final decision.
Pass the selfie or short video you already capture to NeuroVerify through a mobile SDK, a backend SDK or the REST API.
Receive one risk score with signal-level evidence in a single response, typically under 200 ms p95 for eligible image requests.
Map the score to approve, step-up, manual review or decline using thresholds you set.
Attach the result to the application record so audit and fraud teams can revisit the decision.
What you get
Face swaps, synthetic faces and manipulated video are checked in the same request as live presence, so one result covers both questions.
You send the selfie you already collect. Conversion is not asked to absorb another capture screen.
Signal-level evidence shows which checks fired, so analysts spend less time on unexplained flags.
NeuroVerify ranked first of 36 systems on VendorBench-100 (MCC 0.876 versus 0.646 for the next-best vendor).
Choose managed cloud, private cloud or customer VPC, secure container, on-premises or air-gapped deployment.
Two lines to integrate, live in under 24 hours, with SDKs for mobile and backend stacks.
Questions
It checks the selfie, video or audio you already capture for deepfakes and manipulation. It returns one unified risk score with signal-level evidence from six signals in a single request.
It does not check ID documents. Document verification stays with your existing provider.
Liveness answers whether a live person appears to be present. It was not built to answer whether the face, video or audio was generated or manipulated. A face swap, a virtual camera feed or a synthetic video can still pass a liveness prompt.
NeuroVerify includes Live Presence Verification as one of six signals, then adds face manipulation, generative-model and pixel-level analysis in the same request. You keep your existing liveness step and add authenticity evidence to it. See Deepfake Detection vs Liveness Detection.
Most teams send the media they already capture. There is no new step for the end user. NeuroVerify offers native mobile SDKs (Android/Kotlin, iOS/Swift, Flutter), backend SDKs (Python, TypeScript/Node.js, Go, Java), a REST API and an MCP server for AI agents.
Integration is two lines of code, and teams can be live in under 24 hours. That is a product claim; your timeline depends on your own change process.
NeuroVerify targets under 200 ms p95 on eligible image requests, measured under defined test conditions. The test methodology is available on request, so you can compare it with your own latency budget.
Video and audio checks take longer than image checks. Share your media types during evaluation and we will confirm the expected timings.
NeuroVerify can run as a managed cloud API, in a private cloud or customer VPC, as a secure container, on-premises, or air-gapped. Pick the option that fits your security review and data-residency rules. See Deployment and Product data handling.
Neural Defend holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certifications, shown on the Trust page.
Yes. We recommend evaluating on your own captures, including real customer media and the attack types you worry about most. Use your own acceptance criteria rather than a vendor demo set.
For context, NeuroVerify ranked first of 36 systems on VendorBench-100, with a detection score (MCC) of 0.876 against 0.646 for the next-best vendor. Read How to Evaluate Deepfake Detection Vendors for a checklist.
You do. NeuroVerify returns one unified risk score with signal-level evidence. Your own policy decides what to approve, send to review or block. No detector is perfect, so set thresholds against your own risk appetite and review volume.
Because the evidence is signal-level, reviewers can see why a case was flagged instead of facing an unexplained score.
Evaluate NeuroVerify
Send us the selfie media and attack types you care about and see the unified risk score and signal-level evidence on your own captures.