What do India's synthetic content intermediary rules require?
The Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Amendment Rules, 2026 amend the IT Rules, 2021. They were notified by Gazette notification G.S.R. 120(E) dated 10 February 2026 and came into force on 20 February 2026, with corrigenda following on 26 February 2026. The Ministry of Electronics and Information Technology (MeitY) published FAQs the same day, which explain its reading but state that they do not replace the notified text.
The core is a new Rule 3(3), titled due diligence in relation to synthetically generated information. It applies to any intermediary offering a computer resource that enables the creation, modification, publication or sharing of SGI, which MeitY's FAQ says includes AI image and video generators, voice cloning tools and platforms that distribute such content. Those intermediaries must deploy reasonable and appropriate technical measures, including automated tools, to stop users creating or sharing SGI that violates any law. The rule names high-risk categories: child sexual abuse material, non-consensual intimate imagery and sexually explicit content, false documents or electronic records, content about explosives or arms, and SGI that falsely depicts a real person or event in a way likely to deceive.
For SGI that is lawful, Rule 3(3)(a)(ii) requires a clear, prominent label: visible in the display for images and video, and a prefixed audio disclosure for audio. The content must also carry permanent metadata or another technical provenance mechanism, to the extent technically feasible, including a unique identifier that identifies it as SGI and identifies the computer resource used. Rule 3(3)(b) bars intermediaries from letting users modify, suppress or remove those labels or identifiers; the FAQ's example is that a service should not offer "remove watermark" or "export without metadata" features.
| Trigger | Rule | Before | From 20 February 2026 |
|---|---|---|---|
| Court order or reasoned intimation from an authorised government officer | 3(1)(d) | 36 hours | 3 hours |
| Complaint about nudity, sexual, morphed or impersonation content | 3(2)(b) | 24 hours | 2 hours |
| Grievance seeking removal of content under Rule 3(1)(b) | Proviso to 3(2)(a)(i) | 72 hours | 36 hours |
| General user grievance | 3(2)(a)(i) | 15 days | 7 days |
| Periodic notice to users of rules and consequences | 3(1)(c) | At least yearly | At least every three months |
What counts as synthetically generated information under the rules?
Rule 2(1)(wa) sets a realism test. SGI is audio, visual or audio-visual information artificially or algorithmically created, generated, modified or altered using a computer resource, so that it appears real, authentic or true and depicts an individual or event in a way likely to be perceived as indistinguishable from a natural person or real-world event. Deepfake videos, AI-altered photos and cloned voice recordings that meet that threshold are in scope.
The definition carves out routine work. Good-faith editing such as colour correction, noise reduction, compression, transcription or stabilisation is excluded if it does not materially alter the substance, context or meaning. So is routine preparation of documents, presentations and training material, unless it produces false documents or records. Accessibility uses such as subtitles, translation that keeps meaning, and audio description are excluded too. Text-only AI output is not SGI, though general rules on unlawful information still apply to it.
Do large platforms in India have to detect deepfakes before publishing?
Significant social media intermediaries effectively do. New Rule 4(1A) requires an SSMI, before a user displays, uploads or publishes content, to obtain the user's declaration on whether it is SGI, to deploy reasonable and appropriate technical measures, including automated tools, to verify that declaration having regard to the nature, format and source of the content, and to label content confirmed as SGI. MeitY's FAQ says this makes verification explicit: platforms must check declarations rather than rely on self-declaration alone. Its example describes verifying with metadata and detection signals.
The proviso to Rule 4(1A) adds that an SSMI that knowingly permits, promotes or fails to act on SGI in breach of the rules is deemed to have failed its due diligence, which puts the safe harbour under section 79 of the IT Act at risk. The rules also clarify that removing SGI in compliance with them, including through automated tools, does not itself breach the section 79 conditions. SSMI status depends on registered users in India; the threshold set in 2021 is five million.
In practice this creates a detection requirement for the largest services and a strong incentive for smaller ones. Metadata checks catch content from generators that embed provenance. Content from open-source or foreign tools that embed nothing, or content stripped by a screenshot, can only be verified by analysing the media itself.
How does India's DPDP Act apply to deepfake review data?
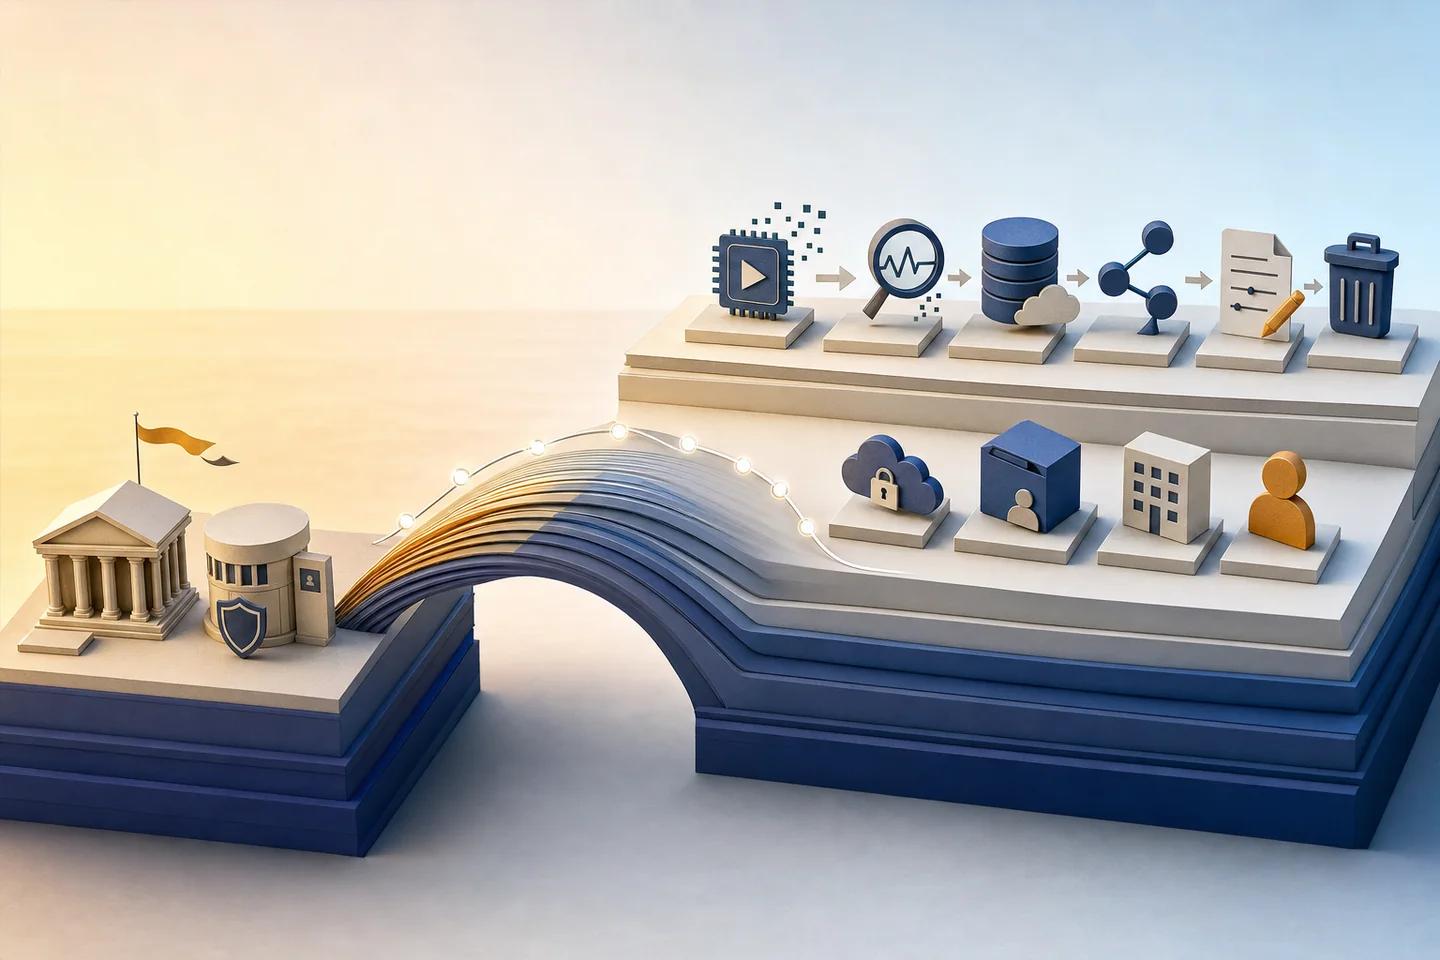
Faces, voices, account identifiers, detection scores and analyst notes collected during SGI review are often digital personal data, so the Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 apply alongside the IT Rules. Commencement is staged. Notification G.S.R. 843(E) brought selected provisions into force on 13 November 2025, scheduled a small group for one year later (13 November 2026), and scheduled most core processing, data principal rights, children's data and enforcement provisions for eighteen months after publication, which is 13 May 2027. The Rules follow the same three groups.
For a platform or a detection vendor, the practical work is mapping roles now: the platform usually acts as data fiduciary deciding purpose and means, and a detection provider as a data processor. Keep only the media and derived data each review step needs, set retention per artifact, and document the purpose for evidence preserved under Rule 3(1)(cb), which asks intermediaries to keep logs and evidence intact when they act against violating users.
What should an intermediary put in place for SGI compliance?
Build the controls around the operative rules and keep the version of the rules and FAQ you relied on with each decision. A workable set looks like this.
- Classify each feature: does it create, modify, host or distribute audio-visual content, and does the service meet the SSMI threshold?
- Add generation-time controls that block the prohibited SGI categories, and record what was blocked and why.
- Apply visible labels and prefixed audio disclosures to lawful SGI, embed metadata and a unique identifier where feasible, and remove any feature that strips them.
- For SSMIs, collect the uploader's declaration and run technical verification before publication, with a review queue for disputed results.
- Staff takedown operations for 3-hour government orders and 2-hour intimate or impersonation complaints, around the clock.
- Preserve logs and evidence when acting against accounts, and give users a grievance and appeal route that meets the 7-day timeline.
How can Neural Defend support SGI verification and review in India?
Pre-publication verification needs speed and evidence. NeuroVerify, Neural Defend's API, checks a face image, video or audio in one call and returns one unified risk score with signal-level evidence from six signals, including Face Manipulation Detection, AI Generative Model Analysis, AI Pixel-Level Manipulation and AI Content Compliance. Eligible image requests return in under 200 ms at p95 under defined test conditions, which fits inside an upload flow. Your policy sets which scores trigger a label, a review or a block; the model does not decide.
Disputed items, grievances and takedown requests need a human-readable record. NeuroDetect, Neural Defend's forensic workspace, lets a reviewer open the file in a case, see heatmaps and attention views down to regions, frames and audio segments, and download a forensic report with observations, uncertainty, provenance and analyst notes. That supports the evidence-preservation and grievance duties without claiming certainty the analysis cannot give.
For data handling under the DPDP Act and sectoral rules, Neural Defend can deploy as a managed cloud API, in a private cloud or VPC, as a secure container, on-premises or air-gapped, and holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certifications. On the public VendorBench-100 benchmark of 100 adversarial still images, Neural Defend ranked first of 36 systems with an MCC of 0.876.
Evidence boundary
Limitations
- This page is an educational reading of the notified rules and MeitY's FAQs, not legal advice. Intermediary classification, safe harbour consequences and specific takedown obligations need fact-specific legal review.
- MeitY describes its FAQ as an evolving document that may change; the notified rules and corrigenda control.
- DPDP commencement dates can be changed by later notification. Check the current notifications before relying on a scheduled date.
- Automated SGI verification produces probabilities and errors in both directions. Reasonable technical measures need a human review path for contested results.
Source record
Sources and references
- Ministry of Electronics and Information TechnologyFrequently Asked Questions on the IT (Intermediary Guidelines and Digital Media Ethics Code) Amendment Rules, 2026Published February 10, 2026. Verified October 19, 2026.
- Ministry of Electronics and Information TechnologyInformation Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, updated 10 February 2026 with corrigendaPublished February 26, 2026. Verified August 7, 2026.
- Ministry of Electronics and Information TechnologyG.S.R. 843(E), commencement notification for the Digital Personal Data Protection Act, 2023Published November 13, 2025. Verified August 7, 2026.
- Ministry of Electronics and Information TechnologyDigital Personal Data Protection Rules, 2025Published November 13, 2025. Verified August 7, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image DetectionPublished July 29, 2026. Verified October 19, 2026.