What deepfake threats do governments face?
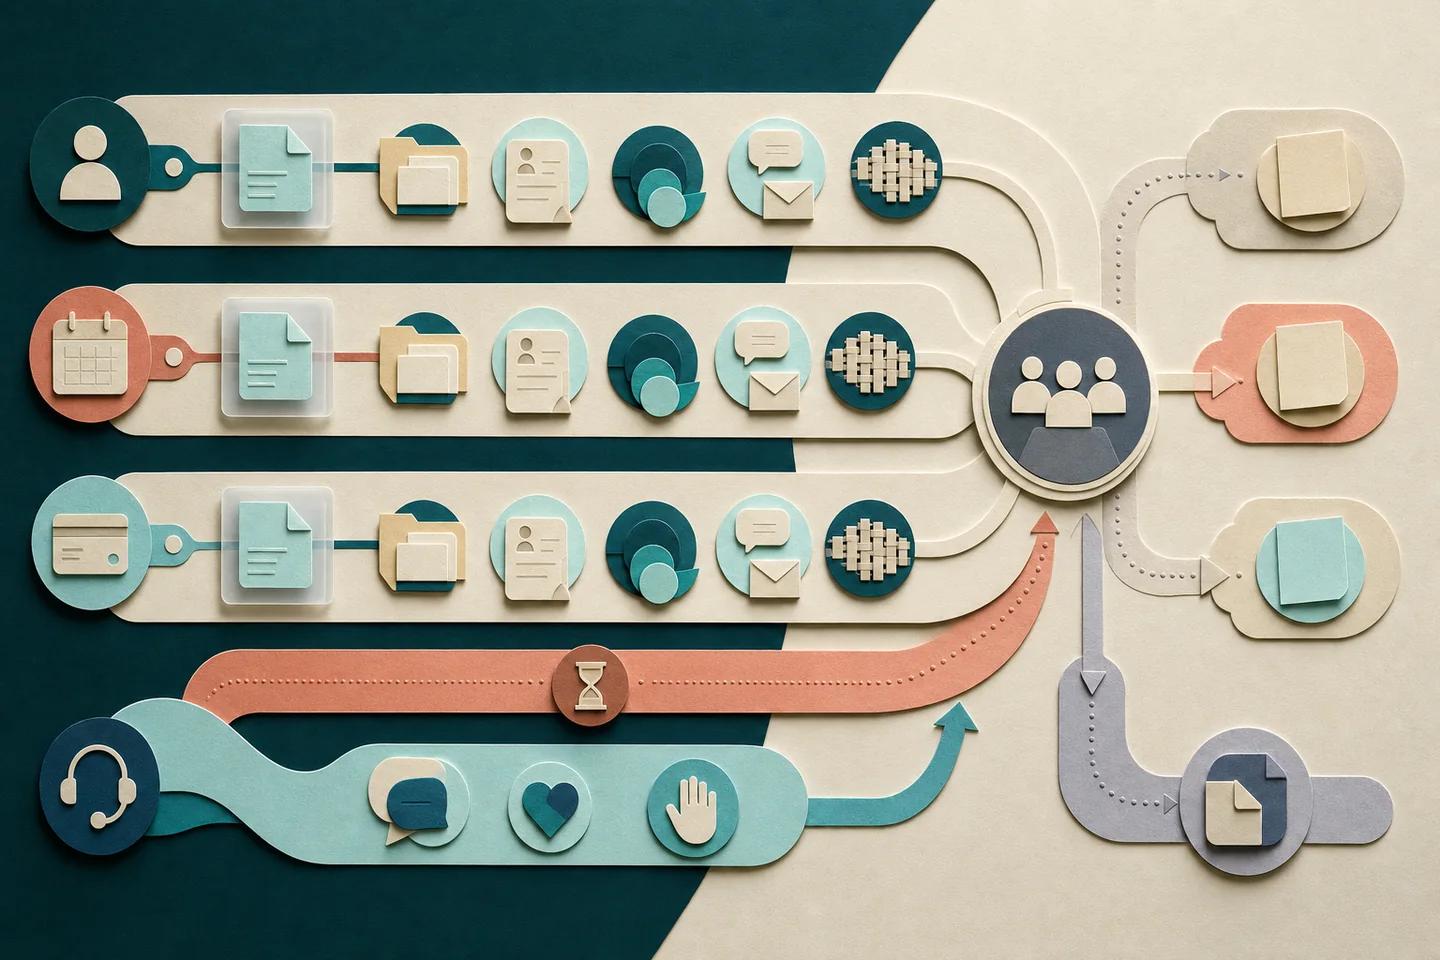
Governments face deepfakes in four forms: fraud against citizen services, impersonation of officials, fabricated official media and synthetic applicants. Each one hits a different team, which is why a single detection tool bought by one department rarely covers the problem.
Fraud against services is the highest-volume threat. Benefit portals, digital licence renewals and tax accounts all accept selfies, ID photos and video from people the agency never meets. FinCEN's November 2024 alert lists unemployment fraud among the schemes funnelled through accounts opened with generative AI identity documents, which shows the same toolkit is used against public money.
Impersonation of officials has drawn the most recent federal warning. In alert I-051525-PSA of 15 May 2025, the FBI said that since April 2025 malicious actors had sent text and AI-generated voice messages impersonating senior US officials, aiming to move targets to another platform and steal account credentials. The analysis of deepfakes targeting US government officials covers that campaign in detail.
Fabricated official media includes fake statements, doctored press footage and synthetic emergency announcements. Synthetic applicants are the fourth form: the FBI reported in June 2022 that deepfakes and stolen personal data were being used in interviews for remote IT roles, a risk for any agency that hires remotely.
| Threat | Typical example | Owning team | Detection lane |
|---|---|---|---|
| Fraud against citizen services | Synthetic selfie in a benefits or licence portal | Digital service and fraud teams | Real-time identity check |
| Impersonation of officials | Cloned voice message from a minister or agency head | Security and communications | Call-back rules plus media review |
| Fabricated official media | Fake video statement during an emergency | Communications and press office | Forensic review and provenance |
| Synthetic applicants | Face-swapped candidate in a remote interview | HR and personnel security | Live video and identity check |
How public-sector teams verify high-risk media and identities
The practical answer is to split verification into two lanes with different speeds and owners. The identity lane answers one question in under a second: is this a live, unaltered person on a genuine device? The media lane answers a slower question that may end up in court or in public: is this recording what it claims to be?
In the identity lane, the agency's enrolment or login flow sends each selfie or video to automated analysis, combines the result with device and session signals, and routes high-risk results to a trained reviewer. The workflow guides on public benefits and government enrolment walk through those steps for specific services.
In the media lane, a suspected fake arrives from a journalist, a citizen report or monitoring. An analyst preserves the original file, checks provenance data such as Content Credentials where present, runs forensic analysis, and writes up findings with the uncertainty stated. The decision to issue a rebuttal or refer a case belongs to a named official, not to the model.
- Identity lane: selfie and video analysis, presentation attack detection, device and capture integrity, reviewer queue.
- Media lane: evidence preservation, provenance check, forensic analysis, written report, accountable sign-off.
What NIST SP 800-63A-4 requires for remote identity proofing
US federal agencies follow NIST SP 800-63A-4, published in July 2025, and many other governments use it as a reference. It sets measurable requirements for remote biometric proofing and treats injected and forged media as a separate threat from people holding photos up to a camera.
Two points stand out for deepfakes. First, PAD testing must conform to ISO/IEC 30107-3:2023, with an impostor attack presentation accept rate below 0.07. Second, the guidance requires controls that raise confidence media came from a genuine sensor, analysis of submitted media for manipulation, and testing of automated image analysis against available attack artifacts with documented false negative rates. NIST also says agencies should analyse media for signatures of generative AI and deepfake tools.
| Requirement | Level |
|---|---|
| PAD meeting an impostor attack presentation accept rate below 0.07, tested to ISO/IEC 30107-3:2023 | SHALL |
| Technical controls that increase confidence media is produced by a genuine sensor, such as detecting virtual cameras or emulators | SHALL |
| Test automated image analysis against available attack artifacts and genuine media, documenting false negative rates | SHALL |
| Introduce random human-in-the-loop cues in remote attended sessions and train agents to spot manipulated media | SHALL |
| Passive detection of forged or manipulated media in all capture scenarios | SHOULD |
| Analyse media for signatures of generative AI algorithms and deepfake tools | SHOULD |
Verifying suspected fake official statements and footage
When a video of an official appears online, speed matters, but so does being right. Start by checking whether the agency itself published it: comms teams should keep an internal register of what was actually released, with original files. A missing original is strong evidence on its own.
Provenance and detection work together. NIST AI 100-4, published in November 2024, describes provenance tracking, watermarking and synthetic content detection as complementary approaches, each with gaps. The EU AI Act adds a disclosure duty: from 2 August 2026, Article 50 requires deployers of deepfakes to disclose them visibly or audibly at first exposure. A hostile actor will ignore that duty, so an unlabeled clip proves nothing. The page on EU AI Act Article 50 explains who must label what.
A forensic tool earns its place when the clip carries no provenance at all, which is the usual case for material circulating on messaging apps. Regional and frame-level evidence lets an analyst explain why a clip was judged manipulated, which matters when the agency's response will be scrutinised.
Deployment, data sovereignty and procurement questions
Public bodies often cannot send citizen biometrics or sensitive evidence to a shared cloud. Ask every vendor which deployment models are supported in production, where models are updated from, and how an air-gapped installation receives new versions. Neural Defend supports managed cloud, private cloud or VPC, secure container, on-premises and air-gapped deployment, scoped during evaluation.
Audit requirements are the other procurement test. A detection result that cannot be tied to a model version is hard to defend in an appeal or tribunal. NeuroDetect keeps model and version context with each analysis and produces a downloadable report with observations, uncertainty, provenance and analyst notes. Neural Defend holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certifications.
Where Neural Defend fits, and what detection cannot settle
For citizen-facing identity steps, NeuroVerify checks a face image, video or audio clip in one request across six signals, including Live Presence Verification, Face Manipulation Detection and AI Generative Model Analysis, and returns one risk score with signal-level evidence. Eligible image requests complete in under 200 ms p95 under defined test conditions. For fake official media and evidence, NeuroDetect gives analysts explainability heatmaps down to regions, frames and audio segments and an LLM-assisted summary linked to evidence, with the analyst making the final call.
Both build on ARCAS 1B, Neural Defend's own detection model; the ARCAS paper reports pooled accuracy of 99.99% on GenImage and 97.74% on Community Forensics. On the public VendorBench-100 still-image benchmark, Neural Defend ranked first of 36 systems with an MCC of 0.876; one benchmark author also co-authored the ARCAS paper.
Detection cannot tell an agency whether a citizen is entitled to a benefit, whether a genuine recording was taken out of context, or whether a real official was coerced. It supplies evidence about manipulation, and agency policy and accountable staff make the decision.
Evidence boundary
Limitations
- NIST SP 800-63A-4 is binding on US federal agencies; other governments may follow different standards, and the thresholds quoted here may not apply to them.
- Detection says nothing about context: a genuine clip used misleadingly will pass manipulation checks.
- NeuroVerify does not analyse ID documents, so document authenticity in enrolment flows needs a separate check or NeuroDetect review.
- Benchmark results cited are for still images and do not measure audio, video or injection attacks.
Source record
Sources and references
- National Institute of Standards and TechnologySP 800-63A-4, Digital Identity Guidelines: Identity Proofing and EnrollmentPublished July 1, 2025. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterI-051525-PSA: Senior US Officials Impersonated in Malicious Messaging CampaignPublished May 15, 2025. Verified October 19, 2026.
- Financial Crimes Enforcement Network (FinCEN)FIN-2024-Alert004: FinCEN Alert on Fraud Schemes Involving Deepfake Media Targeting Financial InstitutionsPublished November 13, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterI-062822-PSA: Deepfakes and Stolen PII Utilized to Apply for Remote Work PositionsPublished June 28, 2022. Verified October 19, 2026.
- National Institute of Standards and TechnologyNIST AI 100-4: Reducing Risks Posed by Synthetic ContentPublished November 1, 2024. Verified October 19, 2026.
- European CommissionTransparency obligations under Article 50 of the AI Act (FAQ)Verified October 19, 2026.
- arXivBenchmarking Neural Defend ARCAS 1B: A Foundational Multimodal Deepfake Detection ModelPublished September 21, 2026. Verified October 19, 2026.