How do provenance, detection and PAD standards differ?
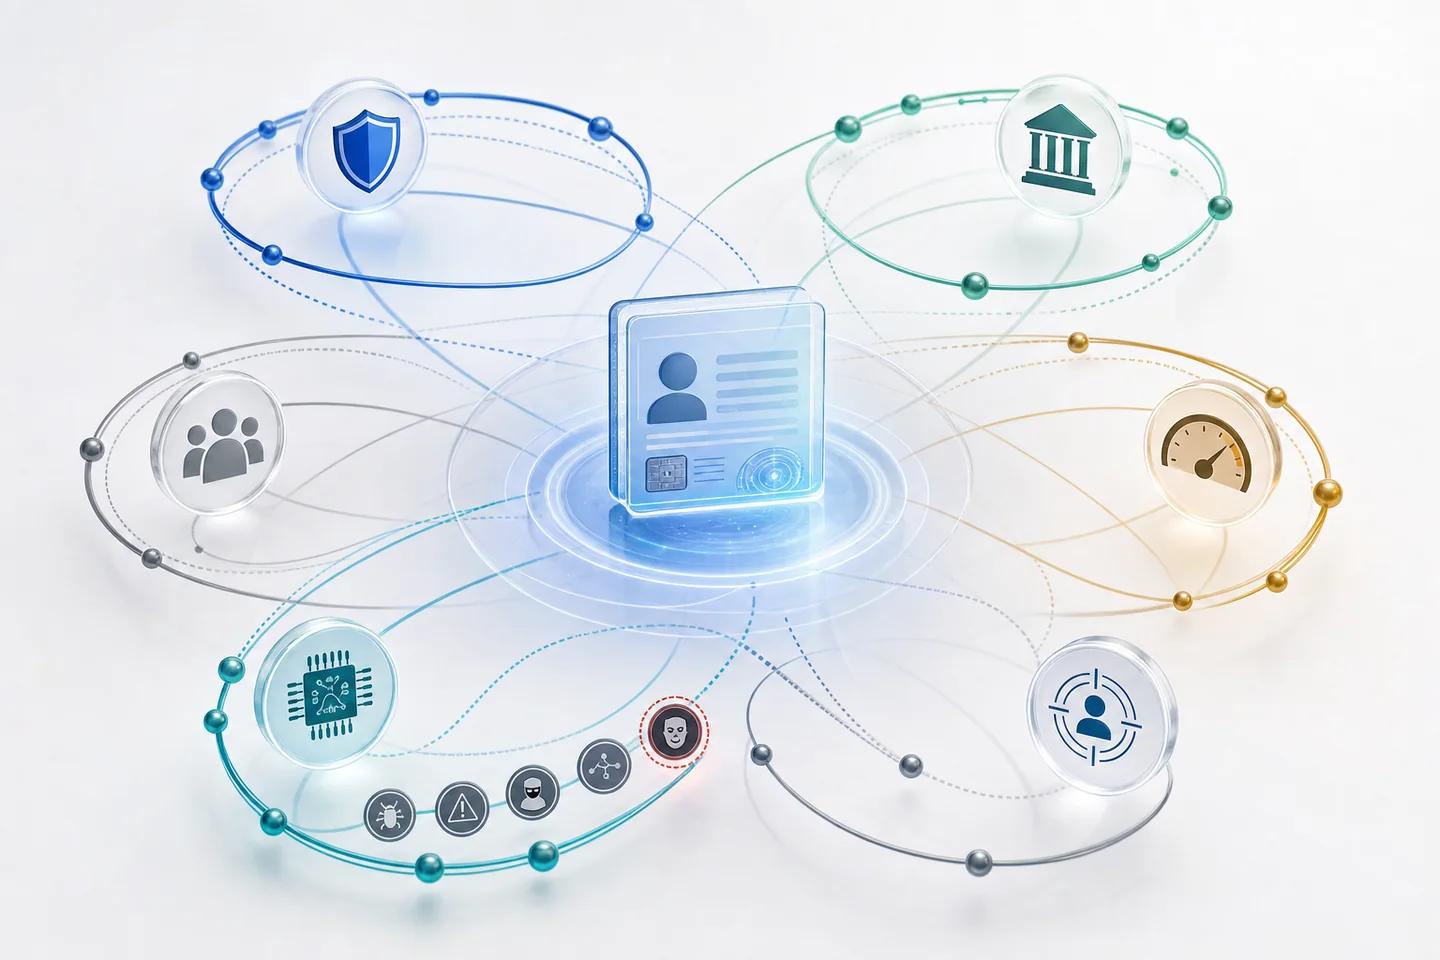
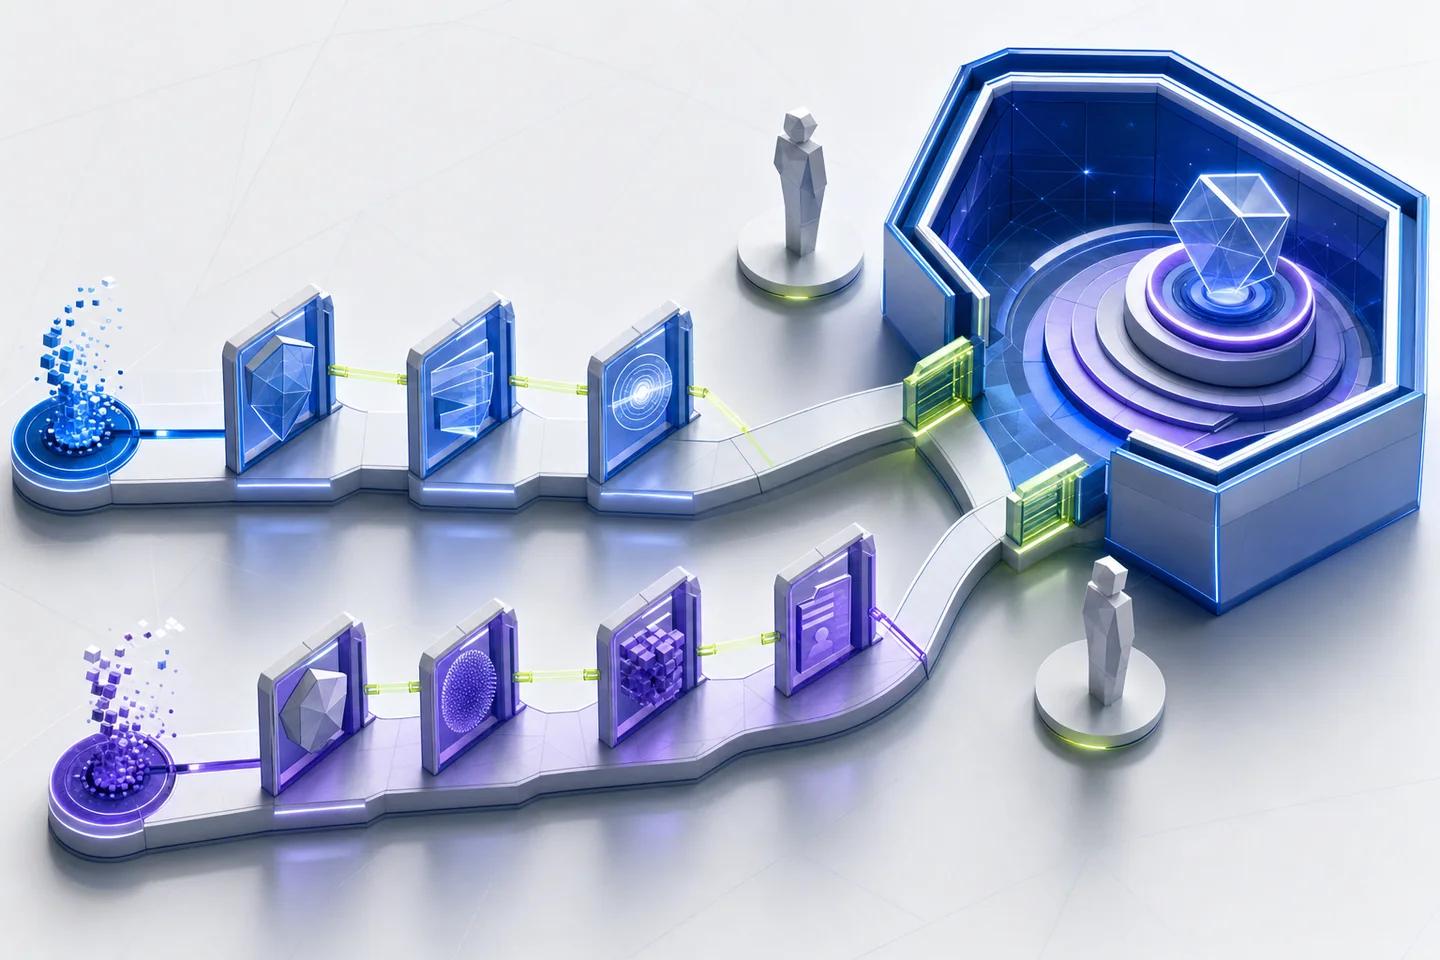
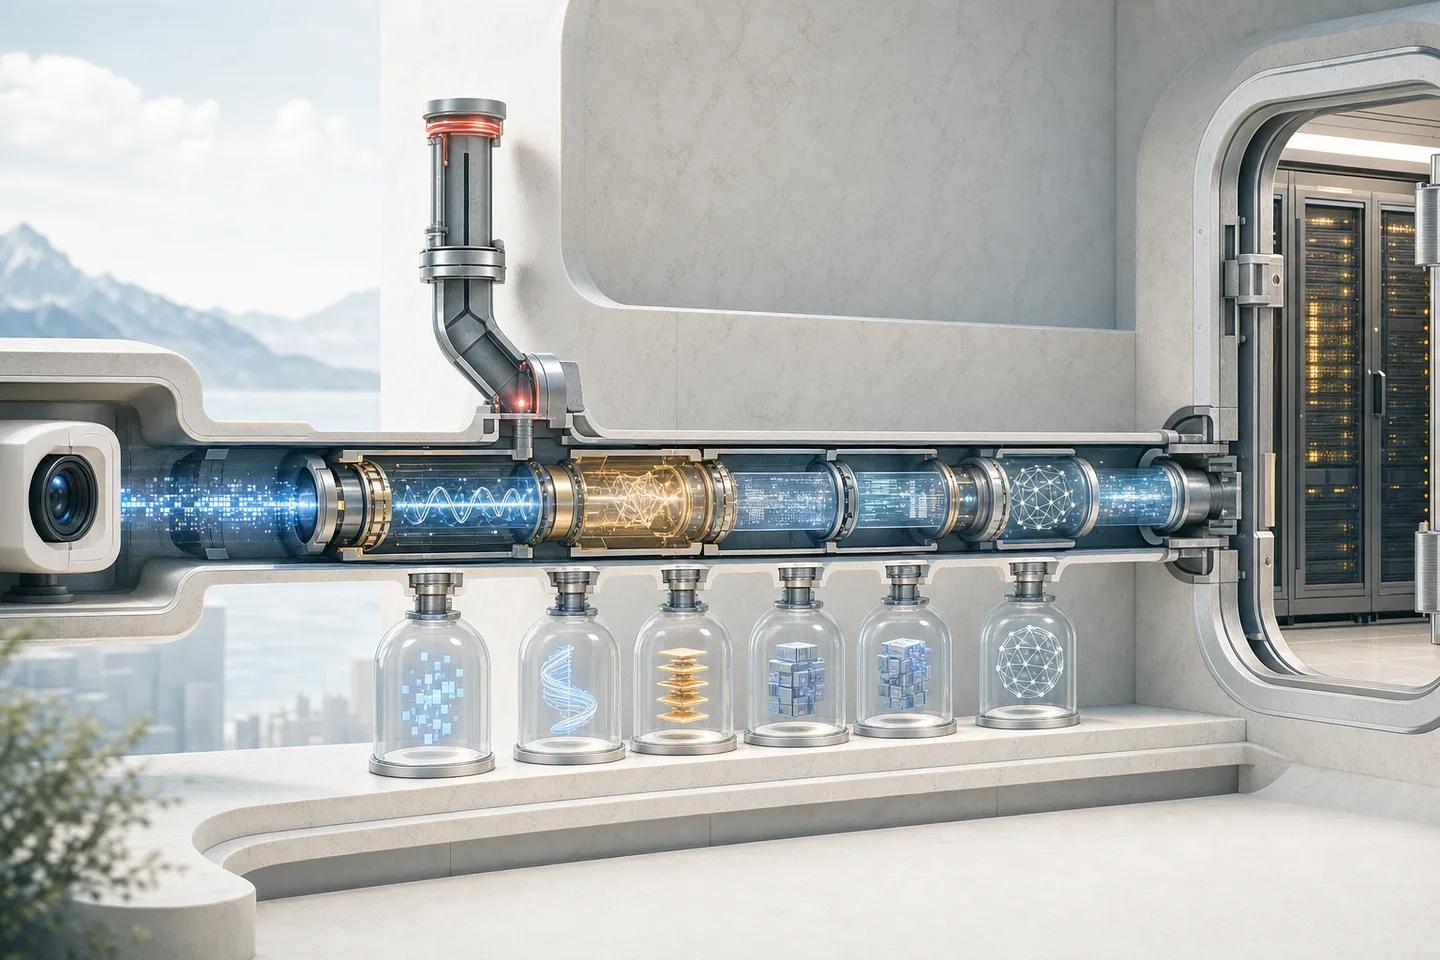
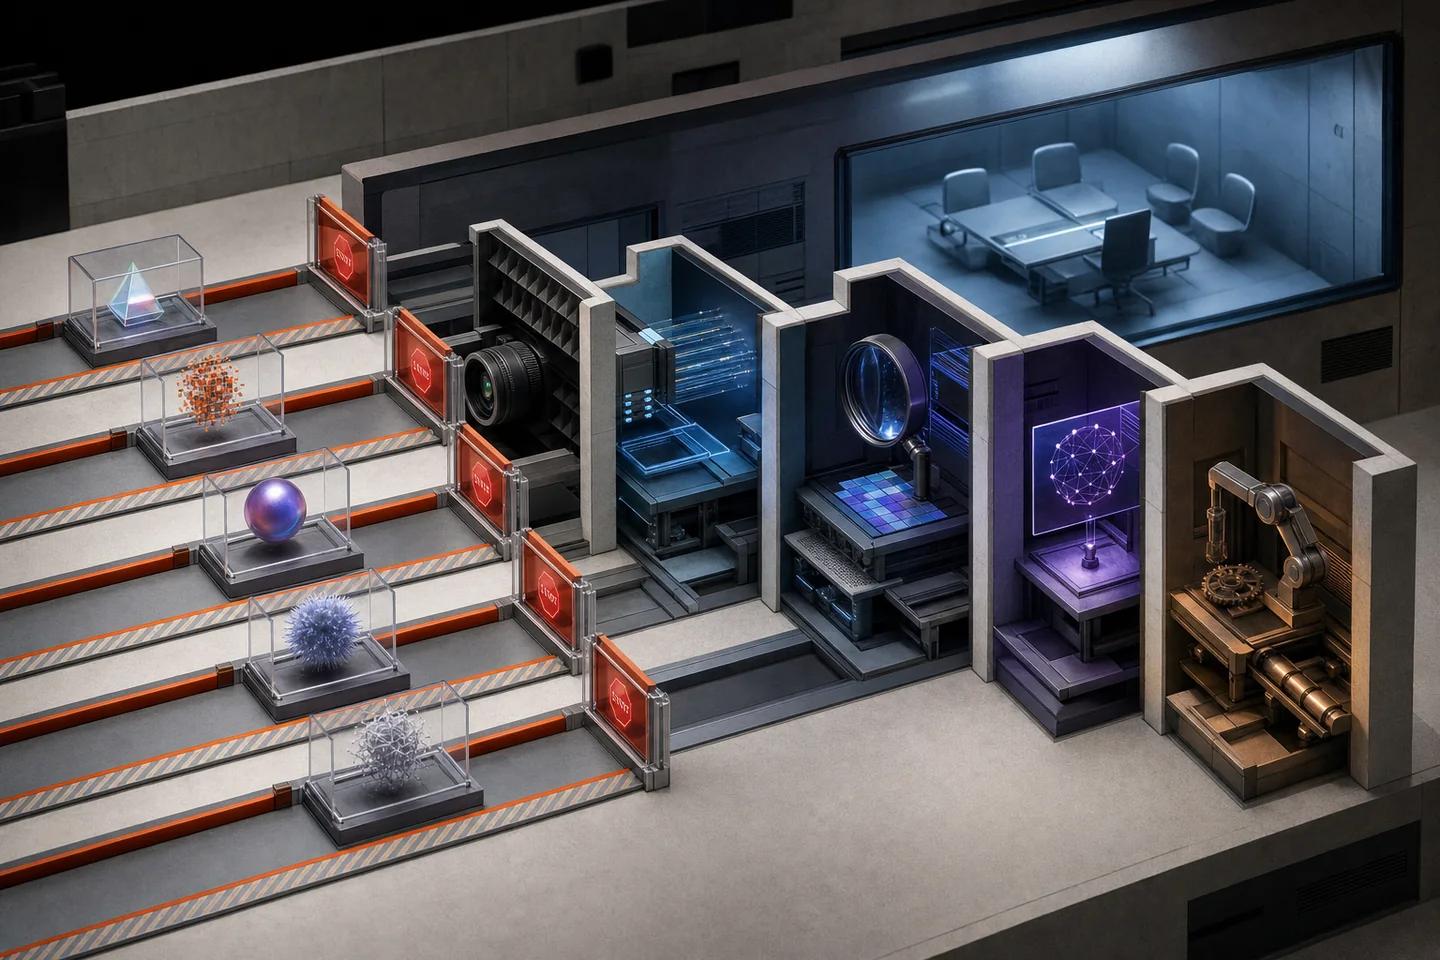
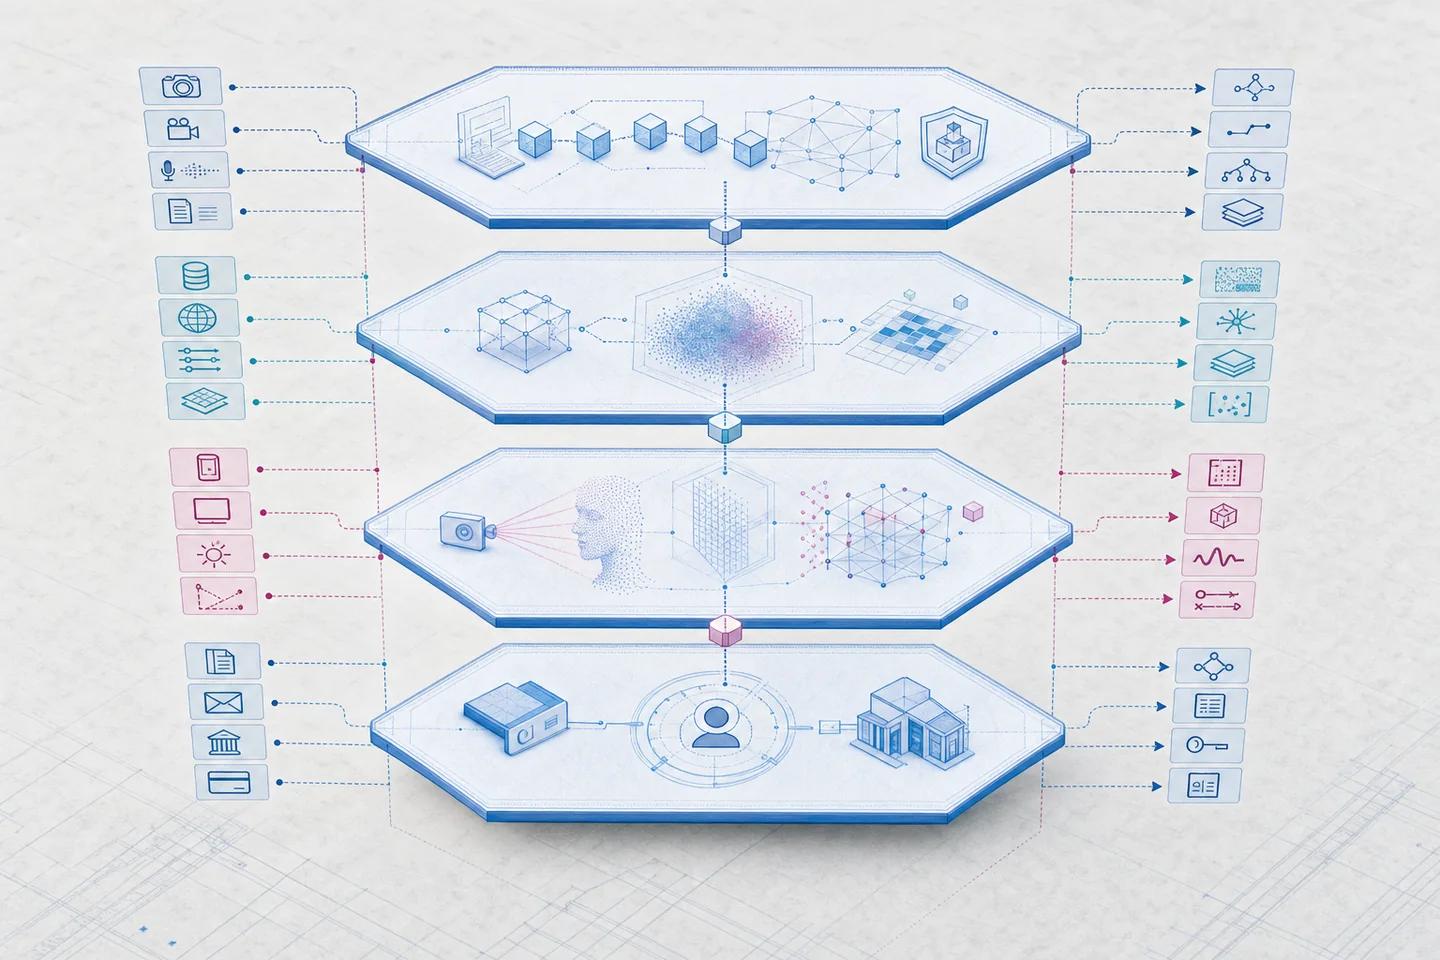
They answer different questions about different points in the media's life. Provenance standards ask what history a file claims and who signed it. Presentation attack detection standards ask whether the thing in front of a biometric sensor is a live person or an artefact. Injection attack detection asks whether the data reaching the biometric system actually came from a genuine sensor. Synthetic media detection asks whether the content itself shows signs of generation or manipulation, wherever it came from.
Deepfakes can attack any of those points. A generated image can carry no provenance at all. A face swap can run live in front of a real camera. A synthetic video can be injected through a virtual camera so the sensor never sees an artefact. And a well-made fake can be uploaded as a file with no capture step to test. That is why a remote identity process, a newsroom or a platform usually needs several layers, each evidenced against its own standard.
| Layer | Standard or guidance | What it covers | What it does not cover |
|---|---|---|---|
| Provenance | C2PA Content Credentials specification (2.4 by July 2026) | Signed, tamper-evident history bound to the file | Truth of the content; files without credentials |
| Presentation attack detection | ISO/IEC 30107-3:2023 | Testing and reporting of PAD against artefacts presented to the sensor | Injected video, face swaps in digital streams, uploaded files |
| Injection attack detection | CEN/TS 18099:2024; ISO/IEC 25456 reported in development | Attacks that bypass the sensor, test plans and evaluation for enrolment and verification | Presentation attacks (left to ISO/IEC 30107) and media authenticity of uploaded content |
| Identity proofing requirements | NIST SP 800-63A-4 (July 2025), section 3.14 | Controls for genuine sensors, analysis of submitted media for manipulation, testing against attack artefacts | A product certification; non-US regimes |
| Synthetic content transparency | NIST AI 100-4 (November 2024) | Survey of provenance, watermarking, detection and testing approaches | Binding requirements |
What does ISO/IEC 30107-3 test, and where does it stop?
ISO/IEC 30107 is the international series on biometric presentation attack detection. Part 1 sets the framework and Part 3, revised in 2023, sets the principles and methods for testing and reporting PAD performance, including metrics such as the attack presentation classification error rate and the bona fide presentation classification error rate. Independent laboratories test liveness products against attack instruments at defined levels, and vendors often cite the resulting conformance letters.
The boundary is the sensor. A presentation attack is something shown to a camera or microphone: a printed photo, a phone screen replaying video, a silicone mask. PAD testing measures how well a system catches those. It does not test what happens when an attacker replaces the camera feed with a synthetic stream, or when a live attacker's face is swapped in software before the frames reach the app. A product can carry a strong 30107-3 result and still be blind to injected deepfakes.
What is CEN/TS 18099 and the ISO/IEC 25456 injection attack detection standard?
CEN/TS 18099:2024, Biometric data injection attack detection, is a European technical specification from the European Committee for Standardization, available from 16 December 2024. It defines biometric data injection attacks and how they affect systems used for enrolment and verification, gives guidance on detecting injection attack instruments and mitigating their risks, and describes how to build test plans to evaluate injection attack detection. It also covers PAD used as a defence and testing how well the system accepts legitimate users. It excludes presentation attack testing, which it leaves to ISO/IEC 30107, as well as evaluation of cryptographic mechanisms such as secure elements.
ISO/IEC 25456 is described by industry sources as the international injection attack detection standard under development to extend this work globally. We could not confirm its stage or publication date from an official ISO listing, so treat claims of ISO/IEC 25456 conformance with care until it is published. In procurement, ask vendors for test reports against CEN/TS 18099 that name the laboratory, the evaluation level, the injection instruments used and the false rejection rate measured.
What does NIST SP 800-63-4 require for deepfakes and injection?
NIST finalised SP 800-63-4, the Digital Identity Guidelines, in July 2025. Section 3.14 of SP 800-63A-4, on identity proofing, states that credential service providers shall implement controls to increase confidence that media comes from a genuine sensor, shall analyse all submitted digital media for artefacts and indicators of manipulation, and shall test automated image analysis against available attack artefacts. It adds that providers should analyse media for signatures of generative AI and deepfake tools, use passive detection in all capture scenarios, and back algorithmic decisions with manual review.
For US federal agencies and the providers that serve them, those are requirements. For everyone else they are a widely referenced benchmark, and FATF's digital identity guidance points regulated entities to assurance frameworks like NIST's when they judge whether remote onboarding is reliable.
How should buyers combine these standards in practice?
Map each threat to a layer, then ask for evidence at that layer rather than accepting one certificate as cover for all of them.
- Presentation attacks: ask for ISO/IEC 30107-3 test results from an accredited laboratory, with the attack levels and error rates.
- Injection: ask for CEN/TS 18099 evaluation reports, plus details of device attestation and virtual camera detection.
- Face swaps and synthetic faces: ask for synthetic media detection results on public benchmarks and on your own capture data, reported with MCC or ROC-AUC rather than accuracy alone.
- Provenance: validate C2PA credentials where present and record their status, without penalising files that lack them.
- Governance: record standard versions, test dates and exclusions, and re-test when generators or capture flows change.
Where does NeuroVerify fit among these standards?
NeuroVerify covers the media analysis layer that NIST SP 800-63A-4 section 3.14 describes and that PAD certification leaves open. One API call analyses a face image, video or audio and returns one unified risk score with signal-level evidence from six signals: Visual Safety Screening, Live Presence Verification, Face Manipulation Detection, AI Generative Model Analysis, AI Pixel-Level Manipulation and AI Content Compliance. Eligible image requests return in under 200 ms at p95 under defined test conditions, so passive analysis can run on every capture, as NIST recommends. Your policy decides the outcome, with manual review where needed.
For benchmark evidence, the public VendorBench-100 benchmark tested 36 systems on 100 adversarial still images, including face swaps, AI photo edits, avatar compositing and opaque-provenance images, and ranked them by MCC because accuracy and F1 are unreliable on that imbalanced set. Neural Defend ranked first with an MCC of 0.876 against 0.646 for the next vendor, with a ROC-AUC of 0.979. One VendorBench author also co-authored Neural Defend's ARCAS 1B paper; the corpus and results are public so anyone can rerun them. VendorBench-100 does not measure video, audio, injection attacks or latency, and it is not a PAD or CEN/TS 18099 evaluation, so pair NeuroVerify with tested PAD and injection controls. Neural Defend holds ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001 and SOC 2 Type II certifications.
Evidence boundary
Limitations
- Standards conformance is bounded by the versions, attack instruments and conditions tested. It does not prove an identity is genuine, content is true, or a legal obligation is met.
- The status of ISO/IEC 25456 could not be confirmed from an official ISO source when this page was updated.
- ISO/IEC 30107-3 and CEN/TS 18099 texts are paid documents; this page summarises their published scope rather than every requirement.
- VendorBench-100 measures still images only and is not a PAD or injection evaluation; one of its authors co-authored Neural Defend's ARCAS 1B paper.
Source record
Sources and references
- Estonian Centre for Standardisation and Accreditation (CEN catalogue listing)CEN/TS 18099:2024, Biometric data injection attack detectionVerified October 19, 2026.
- International Organization for StandardizationISO/IEC 30107-3:2023, Biometric presentation attack detection, Part 3: Testing and reportingVerified August 7, 2026.
- National Institute of Standards and TechnologyNIST SP 800-63A-4: Identity Proofing and EnrollmentVerified August 7, 2026.
- Coalition for Content Provenance and AuthenticityContent Credentials: Deployment Guidance, version 1.0Published July 8, 2026. Verified October 19, 2026.
- National Institute of Standards and TechnologyNIST AI 100-4, Reducing Risks Posed by Synthetic ContentVerified October 19, 2026.
- arXivVendorBench-100: A Unified Cross-Paradigm Benchmark for Deepfake Image DetectionPublished July 29, 2026. Verified October 19, 2026.