What voice cloning attacks look like in 2026
A voice cloning attack uses a synthetic copy of a trusted person's voice to get someone to act: send money, reset a password, share data or open a door. The voice does the persuading that an email or text could not. Attackers gather a few seconds to a few minutes of the target's speech from videos, podcasts, earnings calls or voicemail greetings, generate a clone, and call or leave voice messages for the people who trust that voice.
US agencies have documented the main patterns. The FBI's December 2024 public service announcement describes cloned audio used to impersonate relatives in crisis, well-known public figures and bank customers seeking account access. Its May 2025 alert reported that since April 2025 attackers had sent AI-generated voice messages posing as senior US officials to build rapport and then take over accounts. In January 2024, cloned robocalls imitating President Biden targeted New Hampshire primary voters, and the FCC confirmed on 8 February 2024 that AI-generated voices fall under the TCPA's rules on artificial voices.
How voice cloning attacks differ by industry
The technique is the same everywhere; the target process changes. Map your own exposure by asking which decisions in your organisation can be triggered by a phone call or voice note.
| Sector | Who is impersonated | Process attacked | Control that breaks the attack |
|---|---|---|---|
| Banking and fintech | Customers, relationship managers | Phone banking, account recovery, payment release | Callback to number on file; no voice-only approval of payments or detail changes |
| Corporate finance | CEO, CFO, suppliers | Urgent wire transfers, bank detail changes | Dual approval and out-of-band confirmation for every change |
| IT help desks | Employees, executives | Password and MFA resets, new device enrolment | Identity check through a registered app or manager approval |
| Government | Senior officials and their contacts | Account access, sensitive information requests | Verify through independently sourced numbers; never move to a new app on request |
| Telecom | Account holders | SIM swaps, port-outs, account changes | Step-up verification and notification on a second channel |
The stages of a voice cloning attack
Most attacks follow the same four stages, and each one is a chance to stop them. Reconnaissance comes first: the attacker identifies who can approve what, often from LinkedIn, company websites and press coverage, and collects audio of the person they will impersonate. Next comes the pretext, a believable reason for urgency such as a confidential acquisition, a locked-out executive travelling abroad or a relative arrested overnight.
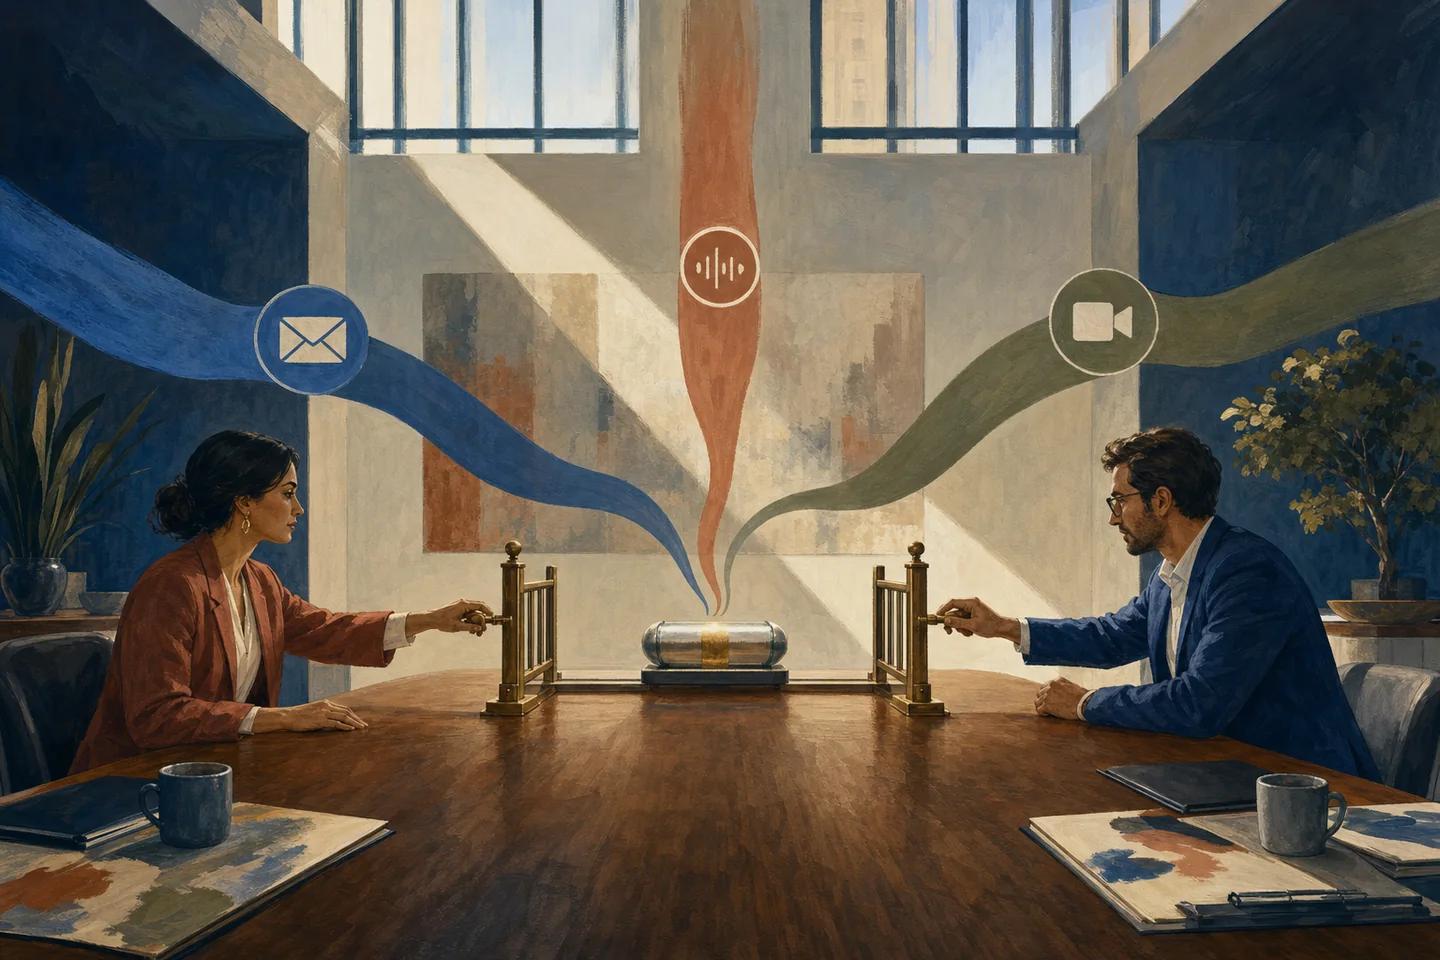
The third stage is contact, frequently across several channels at once: an email or text that sets up the story, then a cloned voice note or call that adds credibility. The final stage is the ask, timed for when the target is busy or alone, with pressure to skip normal steps. Controls placed at the ask, such as mandatory callback and dual approval, are the most reliable because they work regardless of how convincing the earlier stages were.
How can organizations detect voice-cloning attacks?
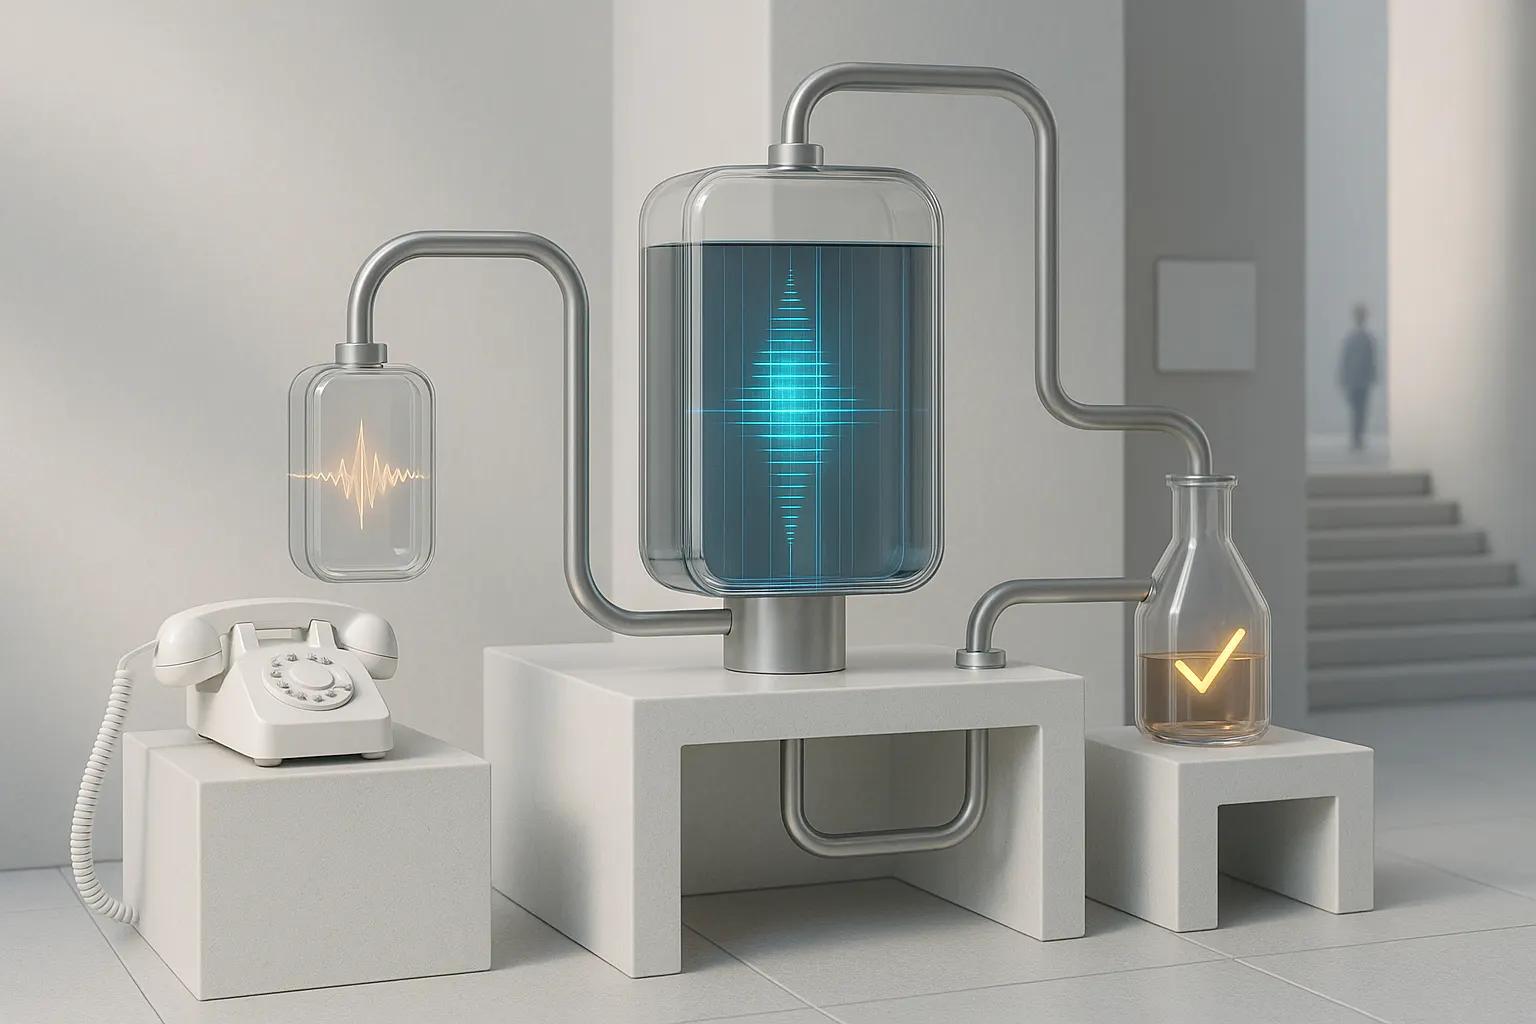
Organisations detect voice cloning attacks by combining three kinds of signal: what the request is, how the call arrived, and what the audio contains. No single signal is enough.
Request signals are the strongest. Urgency, secrecy, a new payment destination, a request to bypass normal approval or to move to another messaging app are the hallmarks the FBI lists. Train staff to treat these as triggers for verification whatever the voice sounds like. Channel signals come from telephony: spoofed or unfamiliar numbers, calls routed through VoIP services, and mismatches between the claimed location and the network data.
Audio signals come from voice deepfake detection, which scores speech for synthesis artefacts that people cannot hear. It is most valuable where call volume makes manual checks impossible, such as contact centres and help desks. Voice biometric matching is not a substitute: NIST's SP 800-63B-4, finalised in July 2025, says voice biometric comparison shall not be used in its authentication guidelines, and a good clone is designed to match.
How to respond when a voice cloning attack happens
Response speed decides the loss. Write a short playbook before you need it and make sure finance, help-desk and security staff know where it is.
- Stop the action. Freeze the payment, reverse the reset or lock the account the call targeted, and contact your bank to recall any transfer.
- Verify with the real person through a known channel and confirm whether anything else was requested from colleagues.
- Preserve evidence: call recordings in original form, voicemails, phone numbers, timestamps and any messages sent alongside the call.
- Warn likely next targets, including the impersonated person's assistants, direct reports and suppliers.
- Report to law enforcement (in the US, ic3.gov) and, for regulated firms, assess whether suspicious activity reporting applies.
- Review the process that let the call succeed and add an out-of-band check to it.
Why voice cloning attacks cannot be fully prevented
Any person whose voice is public can be cloned, and public figures, executives and officials are the most exposed. Watermarking and consent controls in commercial tools help, and the FTC's 2024 Voice Cloning Challenge rewarded ideas such as inaudible watermarks that make cloning harder, but open-source tools carry no such safeguards.
State-backed and organised groups add persistence. The FBI's 2025 alert described a sustained campaign against current and former officials, where compromised accounts were used to reach further contacts. The realistic goal is to make cloned voices useless: no decision of consequence should depend on a voice alone.
Where Neural Defend fits
Neural Defend's NeuroCall, currently in Beta, screens call audio for synthetic speech and returns a risk signal for call-handling rules, so a contact centre or help desk can require a callback or step-up check before acting on a high-risk call. NeuroDetect supports the response side: investigators upload recordings into a case, see evidence down to audio segments, and export a forensic report with model context. NeuroVerify accepts audio with face images and video in one API request for onboarding and account recovery flows.
Deployment options include managed cloud, private cloud or VPC, on-premises and air-gapped installs for teams whose call recordings cannot leave their network.
Evidence boundary
Limitations
- Industry patterns in the table are illustrative of documented attack types, not measured frequencies.
- Audio detection is less reliable on short, noisy or narrowband calls and on new generators, so it must sit alongside process controls.
- NeuroCall is in Beta, and no public benchmark result for its detection is cited on this page.
Source record
Sources and references
- FBI Internet Crime Complaint CenterCriminals Use Generative Artificial Intelligence to Facilitate Financial Fraud (I-120324-PSA)Published December 3, 2024. Verified October 19, 2026.
- FBI Internet Crime Complaint CenterSenior US Officials Impersonated in Malicious Messaging Campaign (I-051525-PSA)Published May 15, 2025. Verified October 19, 2026.
- Federal Communications CommissionDeclaratory Ruling FCC 24-17 on AI technologies and the TCPAPublished February 8, 2024. Verified October 19, 2026.
- NISTSP 800-63B-4 Digital Identity Guidelines: Authentication and Authenticator ManagementPublished July 31, 2025. Verified October 19, 2026.
- Federal Trade CommissionFighting back against harmful voice cloningPublished April 8, 2024. Verified October 19, 2026.
- Starling BankStarling Bank launches Safe Phrases campaignPublished September 18, 2024. Verified October 19, 2026.
- arXivASVspoof 5: Crowdsourced Speech Data, Deepfakes, and Adversarial Attacks at ScalePublished August 16, 2024. Verified October 19, 2026.