Deepfake incident response: the first-hour checklist
The first hour of a deepfake incident decides whether money, access or reputation can still be protected. Use the blocks below as a timetable. They assume someone has just reported a suspicious call, video, voice note or post, or that a payment or account change already happened on the strength of one.
| Time | Goal | Key actions | Owner |
|---|---|---|---|
| 0 to 15 minutes | Stop the consequence | Hold or recall payments, freeze account changes, pause publication, tell the requester's real counterpart | Workflow owner (finance, help desk, communications) |
| 15 to 30 minutes | Preserve and secure | Save native files, URLs, messages and logs; hash originals; reset exposed credentials and revoke sessions | Security operations |
| 30 to 45 minutes | Verify and size | Confirm with the impersonated person through a known channel; check whether others were contacted; gauge public reach | Incident lead |
| 45 to 60 minutes | Notify and hand off | Brief executives, legal and communications; contact banks or platforms; open the investigation and analysis | Incident lead, legal |
Minutes 0 to 15: stop the requested action
Start with the consequence, not the media. If a payment has been sent, call the bank immediately to request a recall; if it is pending, hold it. If credentials or MFA were reset, lock the account. If a statement is about to be published or a file sent, stop it. These steps are reversible if the request turns out to be genuine; a completed transfer often is not.
The Arup case shows why. Hong Kong police said a finance employee joined a video call with what looked like the chief financial officer and colleagues, then made 15 transfers totalling HK$200m to five local bank accounts. Any one of those transfers could have been the moment someone paused and called the real CFO on a known number.
Minutes 15 to 30: preserve evidence and secure accounts
Preserve before anything is deleted. Save voice notes, recordings and images as native files, export chat threads and emails with headers, capture URLs and account IDs, and pull meeting logs and call records. Hash the originals and store them read-only. Do not let anyone edit, forward or re-record the media.
Secure what the attacker touched. Reset credentials and revoke sessions for any account involved, remove mailbox rules created around the incident, and check for new devices or MFA factors. If an executive's account or number was spoofed, warn staff through a verified internal channel.
Minutes 30 to 60: verify, size the incident and hand off
Verify the underlying claim through a channel the attacker does not control: call the impersonated person on a directory number, check with the vendor's record owner, or confirm with the official source. Ask whether other staff, customers or partners received similar contacts, because attackers often try several targets.
By the end of the hour, brief the people who will own the next phase: executive sponsor, legal, communications, and the bank or platform contacts. Open a formal incident with a single timeline that records which channel introduced each instruction, what was done and when. That timeline is the backbone of the investigation and any later report to police, regulators or insurers.
What should a deepfake incident response plan include?
A deepfake incident response plan should include named owners for each high-risk workflow, the verification channels staff must use, evidence preservation steps, decision rules for when to pay, publish or reset, communications templates for internal and public correction, contacts at banks, platforms and law enforcement, and the analysis tools and people who will examine the media.
It belongs inside the existing incident response process rather than beside it. Classify deepfake incidents by consequence (financial fraud, account takeover, false public media, harassment or extortion), map each to an owner, and add the steps that are specific to synthetic media: media preservation, forensic analysis and public correction.
The NSA, with contributions from the FBI and CISA, published the information sheet Contextualizing Deepfake Threats to Organizations on 12 September 2023 to help organizations identify, defend against and respond to deepfake threats. It is a useful reference when writing the plan and briefing leadership.
- Scope and incident categories, ranked by consequence.
- Named owners and deputies for finance, identity, communications, legal and security.
- Approved verification channels and call-back directories.
- Evidence preservation and chain-of-custody steps.
- Decision rules for payment holds, account locks and public statements.
- Pre-drafted internal and external correction templates.
- External contacts: banks, platforms, law enforcement, insurers.
- Analysis tools, access and who signs off findings.
- Exercise schedule and post-incident review.
Bringing in forensic analysis
Analysis usually starts after the first hour, once the consequence is contained and evidence preserved. It answers questions that shape the rest of the response: which artifacts were synthetic, whether a recording of an executive is genuine, and what to say publicly.
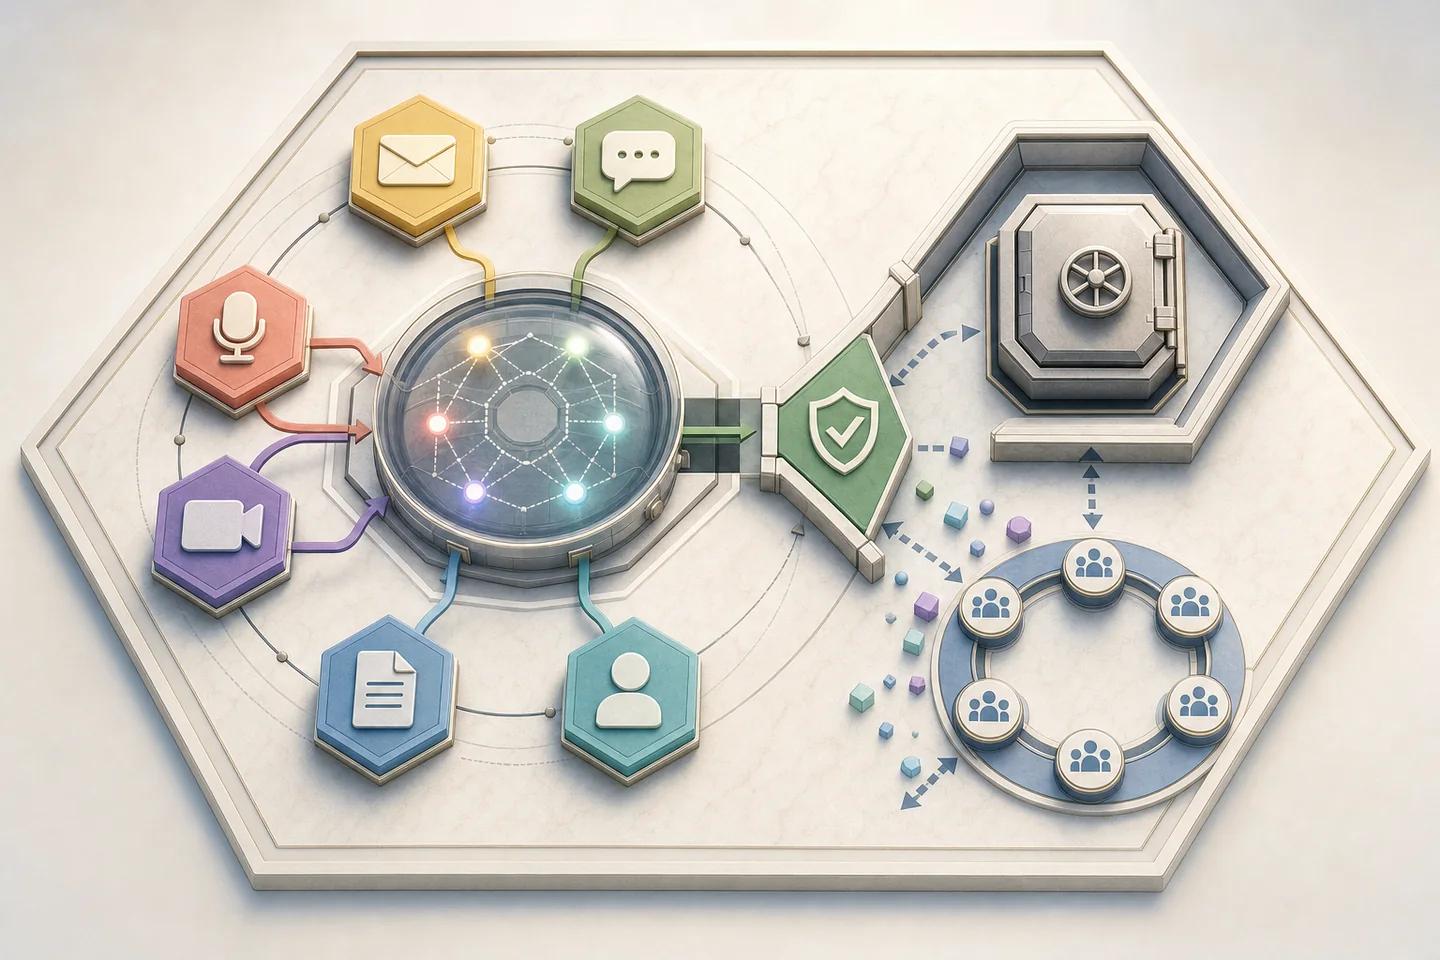
Neural Defend's NeuroDetect is a forensic workspace for that phase. The incident team uploads authorized images, audio, video and documents into one case; each analysis keeps model and version context; heatmaps and attention views show findings down to regions, frames and audio segments; and an LLM-assisted summary links statements to the evidence while the analyst makes the final call. The forensic report covers observations, uncertainty, provenance, model context and analyst notes, ready for legal, insurers or police. Deployment can be managed cloud, private cloud, on-premises or air-gapped.
Detection results inform decisions; they do not make them. A synthetic finding supports a correction or a fraud claim. A clean result on a compressed clip does not clear a request that skipped verification.
Exercising the plan
Run a tabletop or live exercise at least once a year. A realistic scenario starts with an email from a lookalike executive account, moves to a voice note and then a short video call, and ends with an urgent payment or a password reset. Measure how long it takes for someone to stop the action, whether staff use the approved verification channel, whether evidence is preserved correctly, and how quickly a correction could go out.
Review every real incident and near miss within two weeks. Update the plan, the verification directory and the training material, and share lessons with the teams most likely to be targeted next.
Evidence boundary
Limitations
- Timings in the checklist are a guide; complex incidents may need longer for verification.
- Bank recalls and platform removals are not guaranteed, even with fast action.
- Forensic analysis of compressed or partial copies may be inconclusive and should not delay containment.
Source record
Sources and references
- Cybersecurity and Information Systems Information Analysis Center (republishing NSA)NSA, U.S. Federal Agencies Advise on Deepfake ThreatsVerified October 19, 2026.
- The GuardianUK engineering firm Arup falls victim to £20m deepfake scamVerified October 19, 2026.
- Federal Bureau of Investigation Internet Crime Complaint CenterCriminals Use Generative Artificial Intelligence to Facilitate Financial Fraud (I-120324-PSA)Verified October 19, 2026.
- Scientific Working Group on Digital EvidenceGuidelines for Forensic Image AnalysisVerified August 7, 2026.
- National Institute of Standards and TechnologyReducing Risks Posed by Synthetic Content (NIST AI 100-4)Verified October 19, 2026.